RemotePower is the open-source, all-in-one, Swiss-army-knife control plane for your Linux, Windows and macOS fleet — monitoring with alerting, a CMDB, documentation with RAG search, CVE scanning, patching and remote management in one place, with AI woven through all of it (entirely optional). Self-hosted and MIT-licensed: no SaaS, no agents phoning home, no per-node pricing.
Demo login: demo / demo — read-only sandbox that resets periodically.
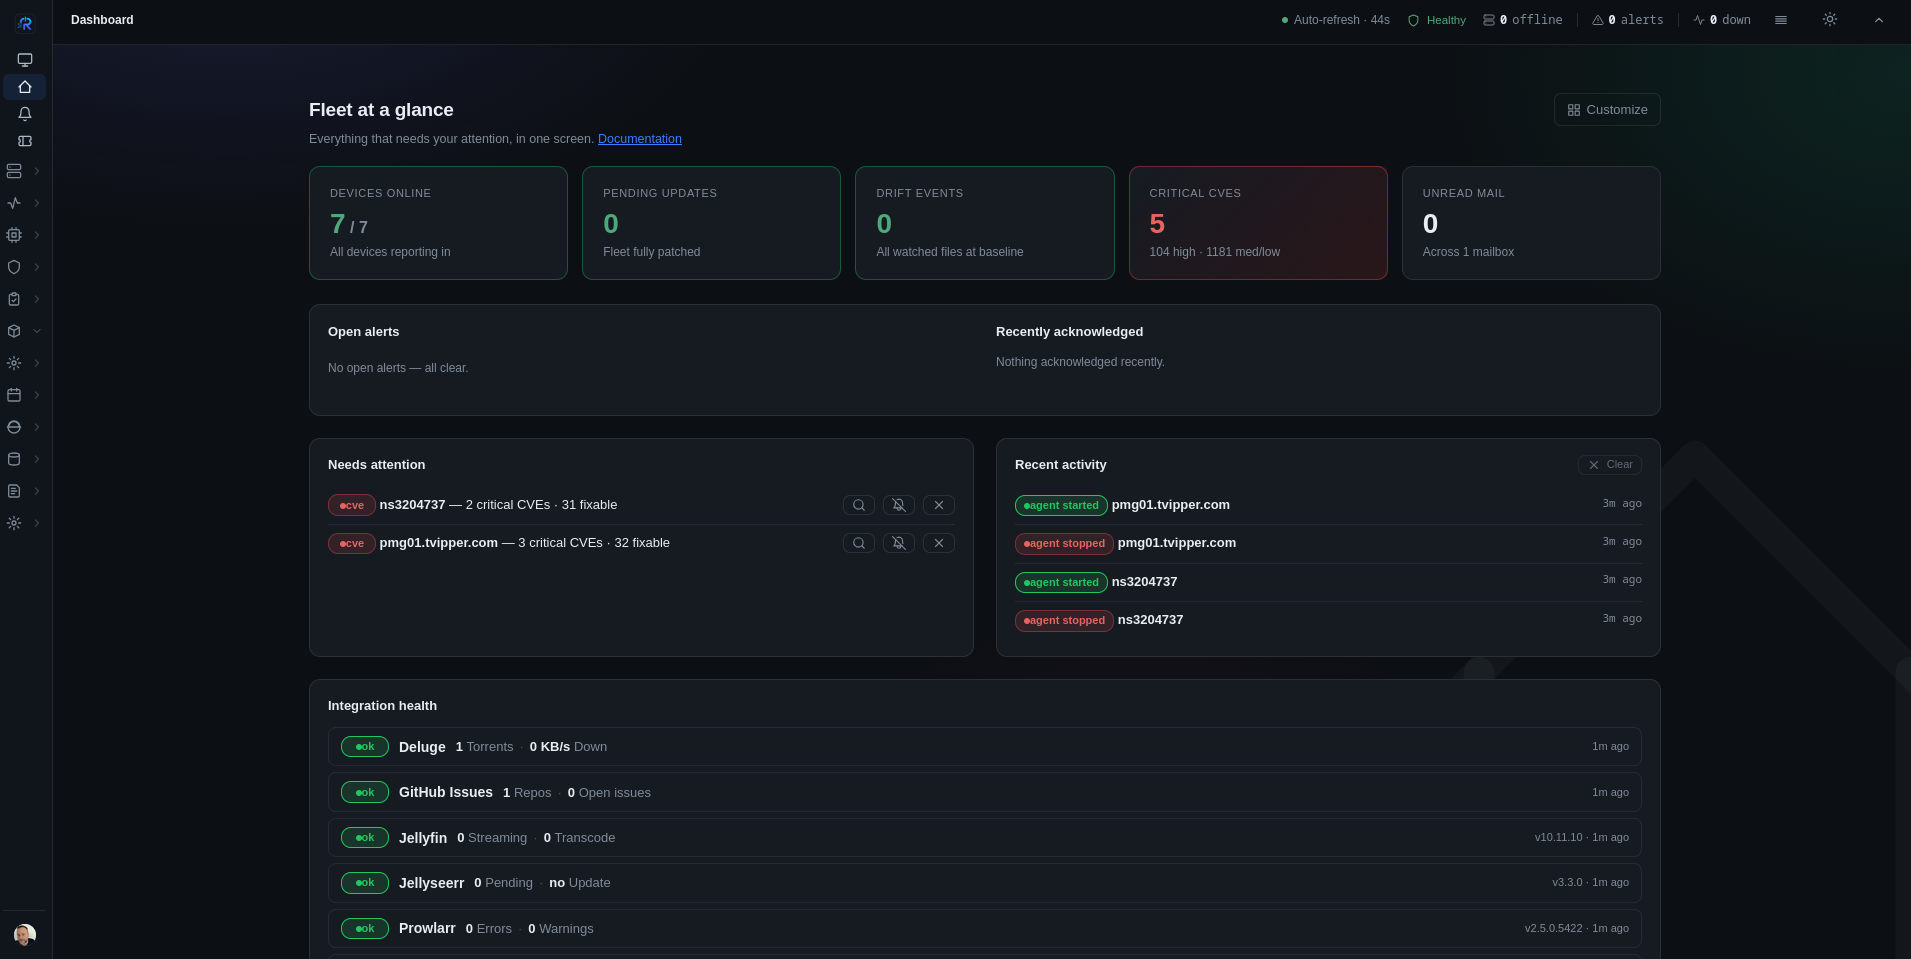
Most teams stitch together a monitor, a CMDB, a wiki, a vulnerability scanner, a patch tool and an SSH jump box. RemotePower is the Swiss-army-knife that does all of it — monitoring & alerting, CMDB, documentation with RAG, CVE scanning, patching and remote management — from a single host you control, with AI on tap throughout.
Check-ins every 60s with CPU / RAM / swap / load sparklines, a service matrix, and a fleet-events timeline. Trends charts plot memory, swap, disk and CPU-load history per host.
Per-disk SMART with failing / pre-fail alerts, kernel-reboot & livepatch awareness, a passive DIMM / temp / RAID inventory, and ZFS / mdadm / btrfs pool health with scrub-overdue and degraded-array alerts.
Projects per-mount disk-fill — "/ fills in ~18 days" — and flags hosts whose memory, swap or disk jumps far outside their own normal range.
Fleet-wide thermal roll-up (hottest hosts), UPS / GPU power draw with a per-group energy-cost chargeback, a predictive disk-failure ETA from SMART trends, and an SSH-key audit (fingerprints, weak & reused keys) across every host.
Tail any unit or file with regex alerting, and see exactly what's listening on every host with change detection.
Every listening socket classified world / LAN / local by its bind address — with an alert the moment a service first becomes world-reachable, and a host firewall-ruleset drift fingerprint.
OSV.dev-backed, severity-ranked findings per host with a per-CVE ignore list, now prioritized by real-world risk — a daily CISA KEV + EPSS join puts exploited-in-the-wild CVEs first. Plus CycloneDX / SPDX SBOM export per host or fleet.
A 0–100 fleet health score, scheduled posture reports, and PCI / HIPAA / SOC 2 controls — or a real OpenSCAP CIS / STIG scan — scored pass / fail with evidence.
Shutdown, reboot, Wake-on-LAN, arbitrary shell, multi-line scripts with a dry-run lint — single host or batched across many, now or on a schedule.
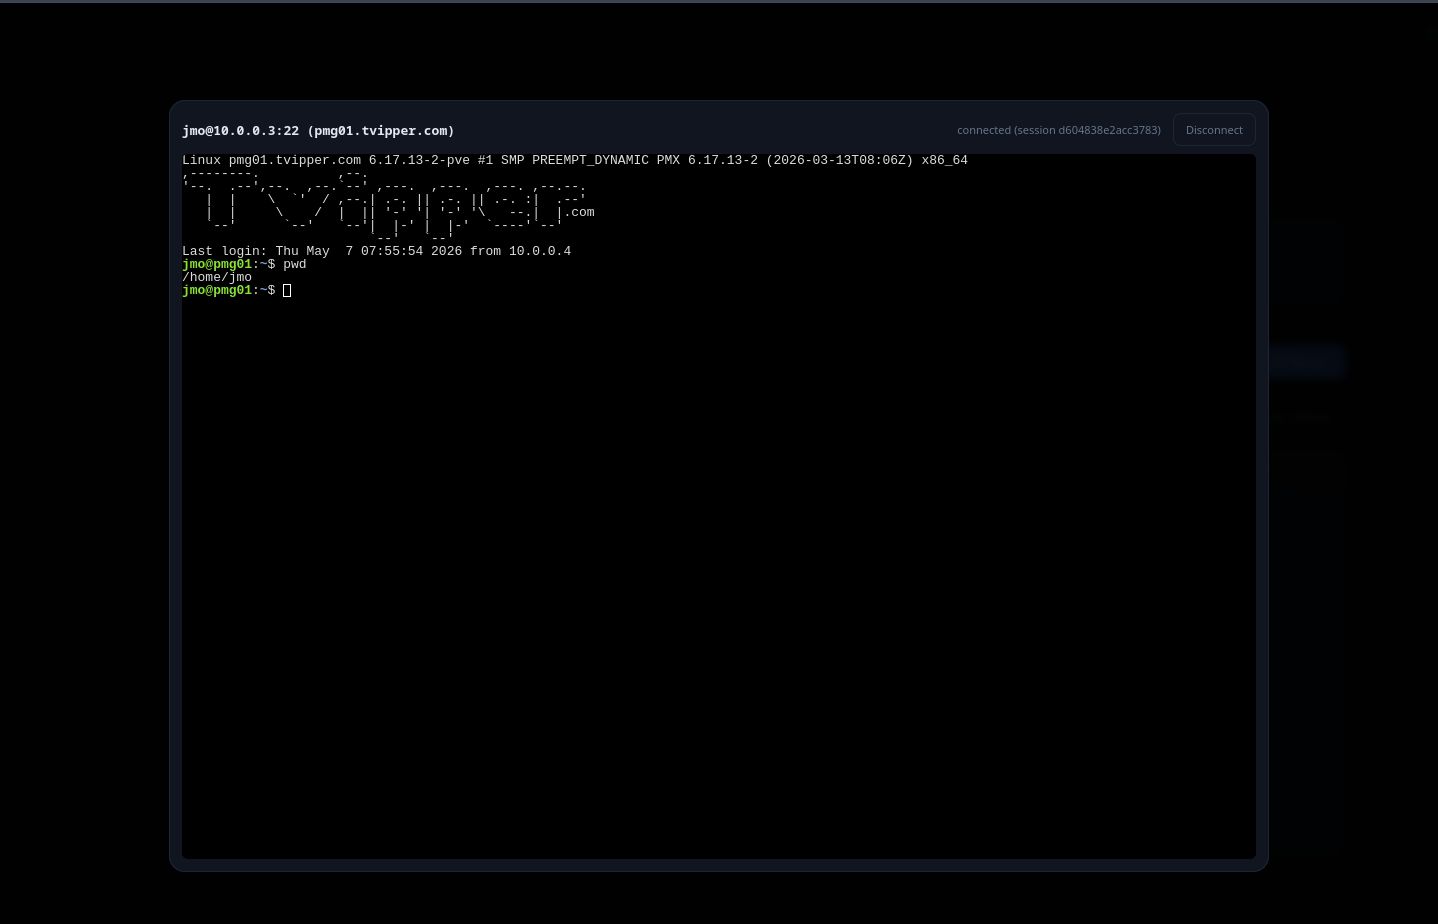
A real xterm.js terminal proxied through a hardened daemon — no client to install — with session recording.
Start / stop / snapshot VMs and containers across Proxmox, VMware vSphere / vCenter, VMware Cloud Director and OpenShift / KubeVirt — plus create VMs or LXC from a wizard and watch for stale backups. Server-to-API, admin-only, SSRF-guarded, audited.
Start / stop / restart Docker & Podman, deploy docker-compose stacks, watch for stale image updates with one-click pull-and-recreate, and see per-container restart counts to spot crash loops.
Staggered rolling patch waves, scheduled auto-patch, optional maker-checker approval for risky changes, and per-device Let's Encrypt issuance / renewal via DNS-01.
Browse & transfer files over SFTP, run restic / borg / rsync backups, manage host users, SSH keys and firewall ports, and enforce desired-state config on drift.
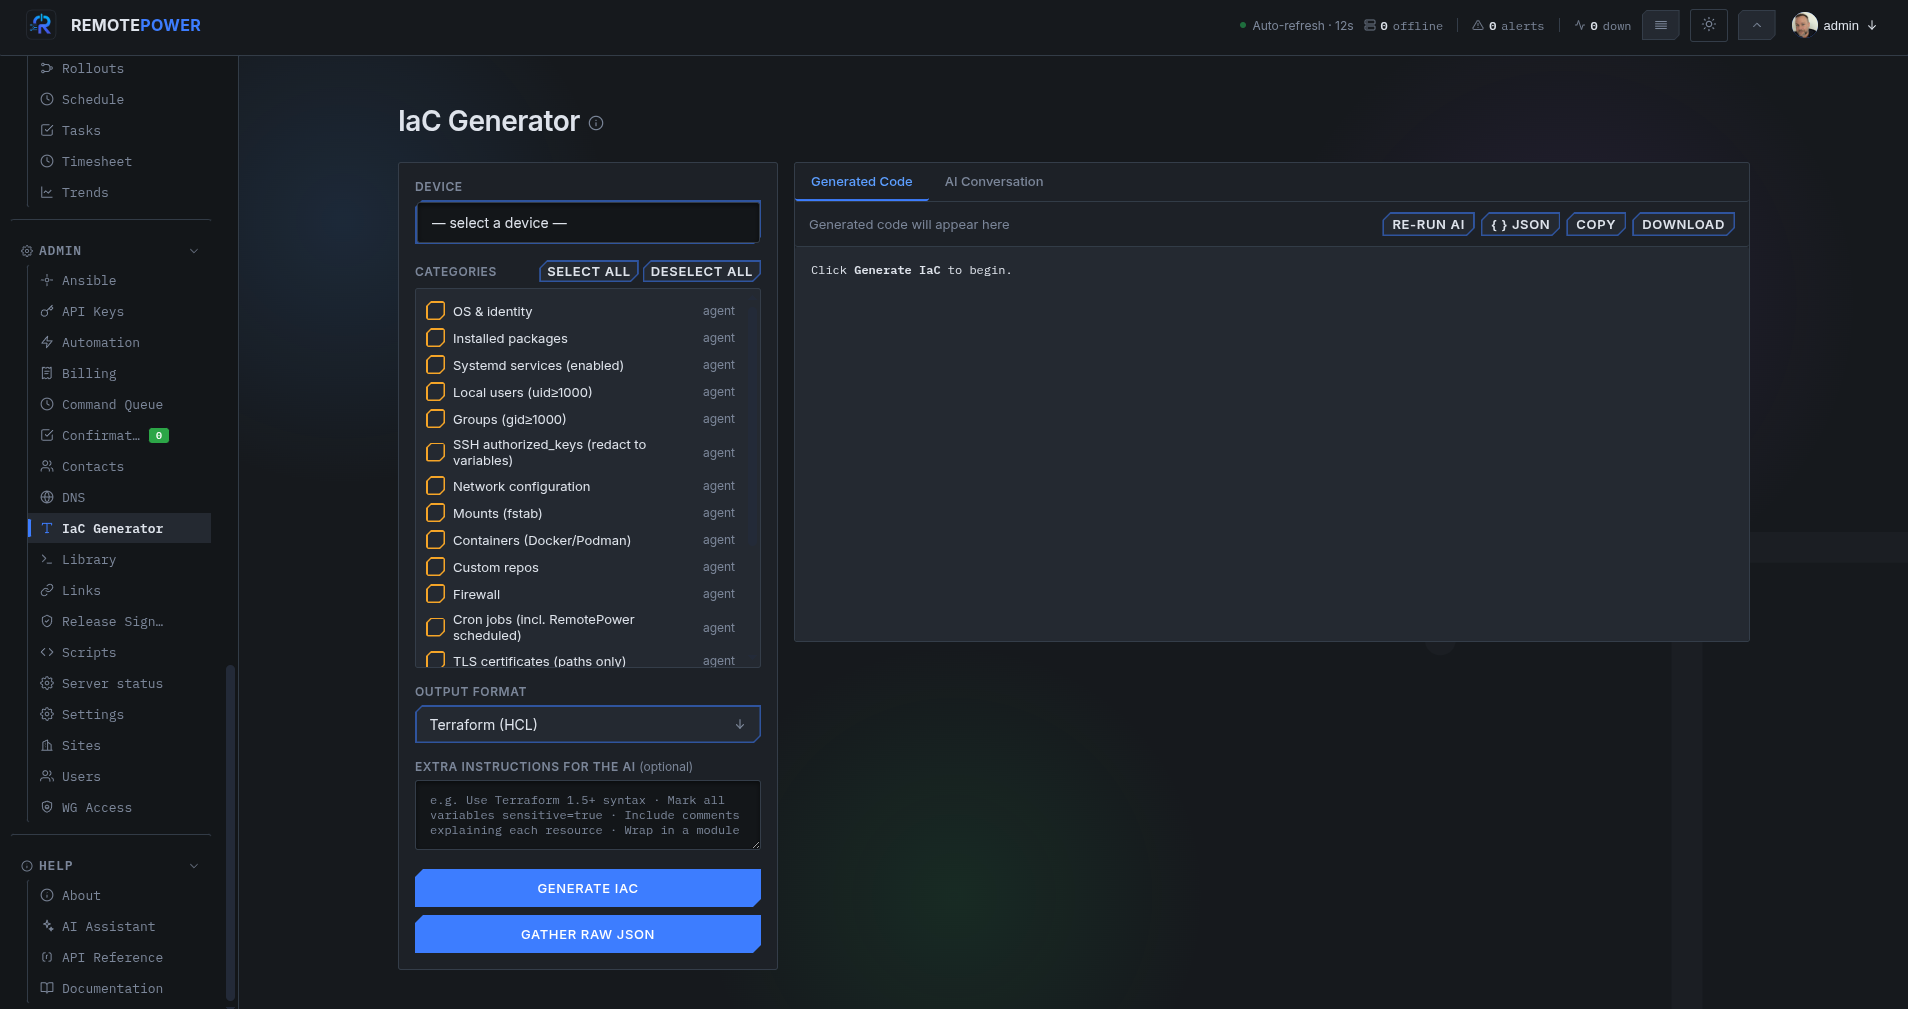
Run Ansible playbooks fleet-wide with the server as control node, write bash health checks that run every few minutes, and export your inventory as Terraform / Ansible / Pulumi / cloud-init.
Stay zero-dependency on flat JSON, step up to embedded SQLite, or run PostgreSQL with automatic failover and read replicas — pooled through PgBouncer, behind load-balanced app nodes, reaching segmented networks through relay satellites. The same push-based agents throughout. macOS joins the Linux & Windows agents.
bcrypt + TOTP 2FA with one-time recovery codes, passkeys (WebAuthn) for phishing-resistant passwordless sign-in, LDAP / Active Directory, OIDC and SAML 2.0 SSO (Okta, Entra, OneLogin, Ping, ADFS) with SCIM deprovisioning, per-role MFA enforcement, session caps, API-key expiry, and named API keys with custom scoped roles.
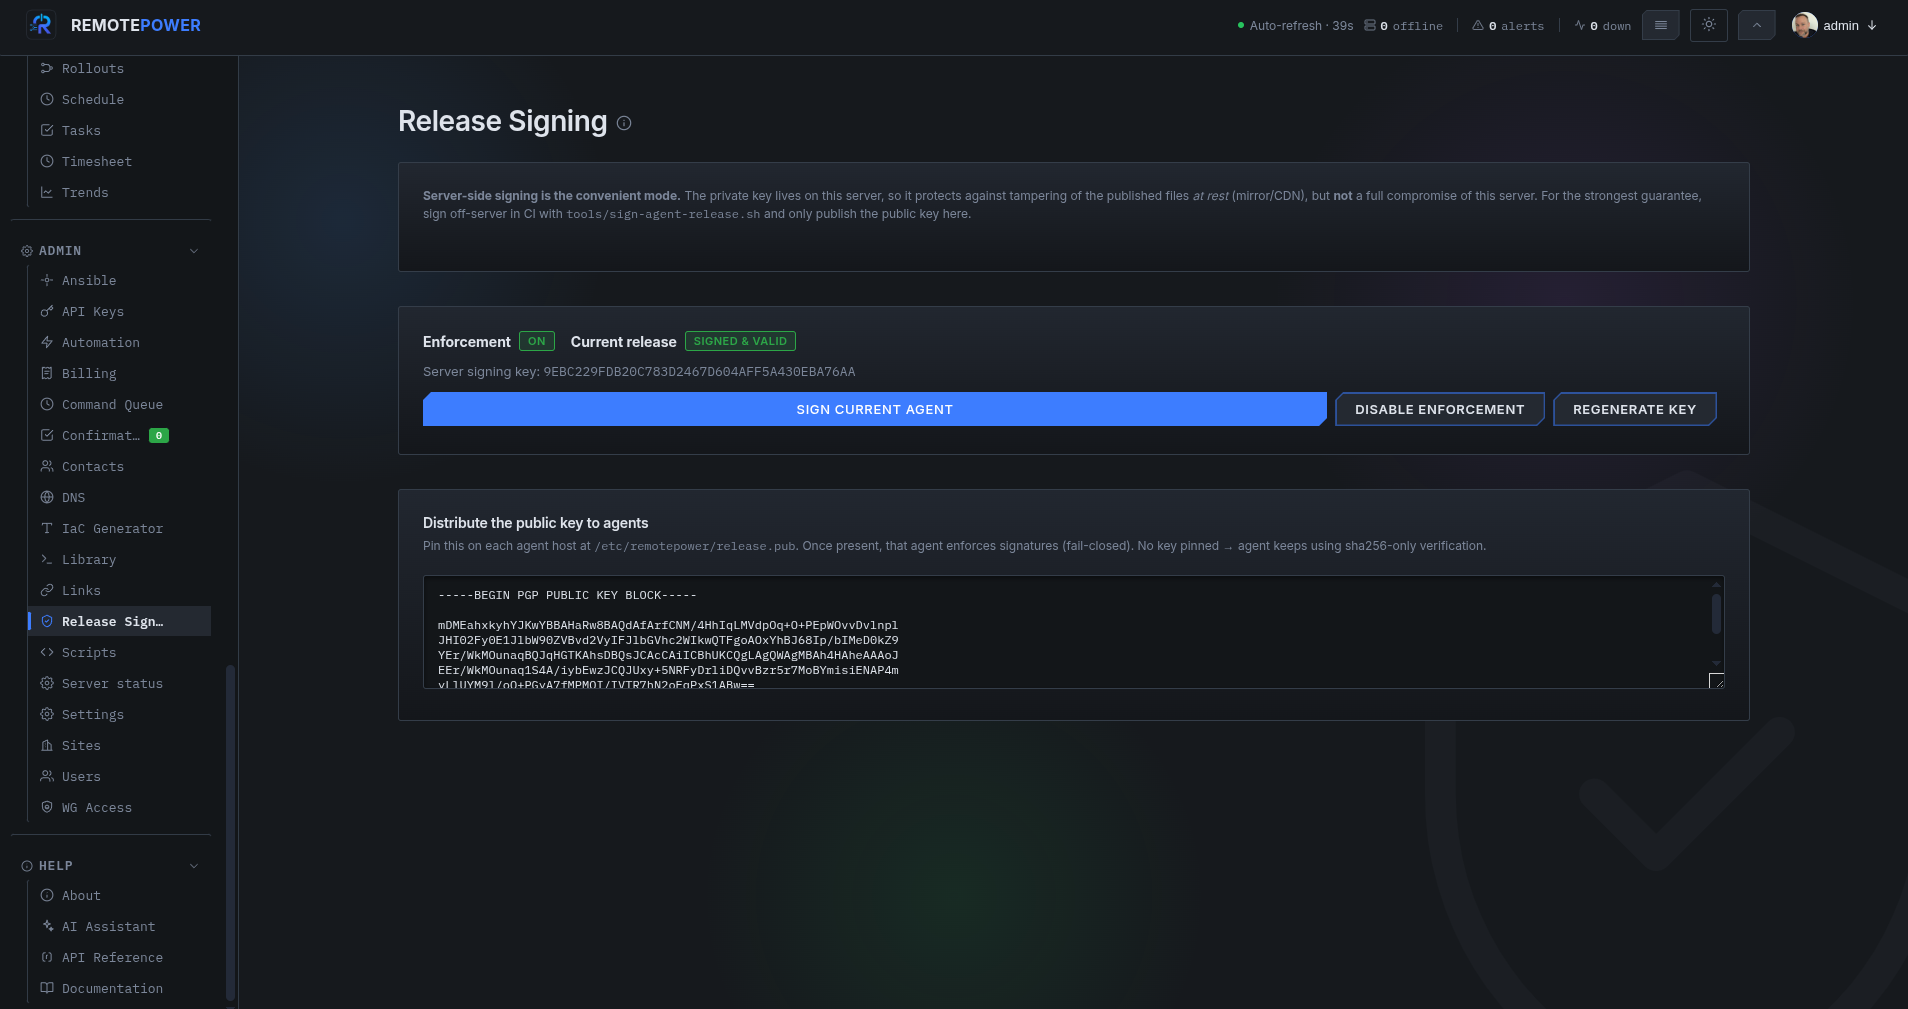
PBKDF2 / bcrypt passwords, session tokens hashed at rest, AES-GCM vault, brute-force lockout, IP allowlist, strict CSP with no inline code, anti-DNS-rebinding SSRF guards, sandboxed SCAP reports, OIDC claim checks, and opt-in signed agent updates. Every hop can run over TLS — including the agent→satellite relay. Externally scanned (Bandit, ZAP, Nikto, Nuclei, Wapiti) with no exploitable findings.
File-integrity monitoring and baseline checks — file-hash, directory, web-root code and egress tripwires that fire on a name you've never seen, apply by scope from a catalog, and stop when you disable them. Plus first-class OS security posture scored as Checks across Linux, macOS (FileVault, Gatekeeper, SIP) and Windows (Defender, BitLocker, tamper protection, Secure Boot, UAC).
Banned / required / min-version package rules over the existing inventory, new-source-IP login alerts, and a scheduled-job (systemd timer) failure lens — all edge-triggered, optionally tag-scoped.
Every privileged action is recorded — who, what, when — with optional forwarding to a SIEM or syslog collector, and one-click quarantine to freeze a suspect host server-side.
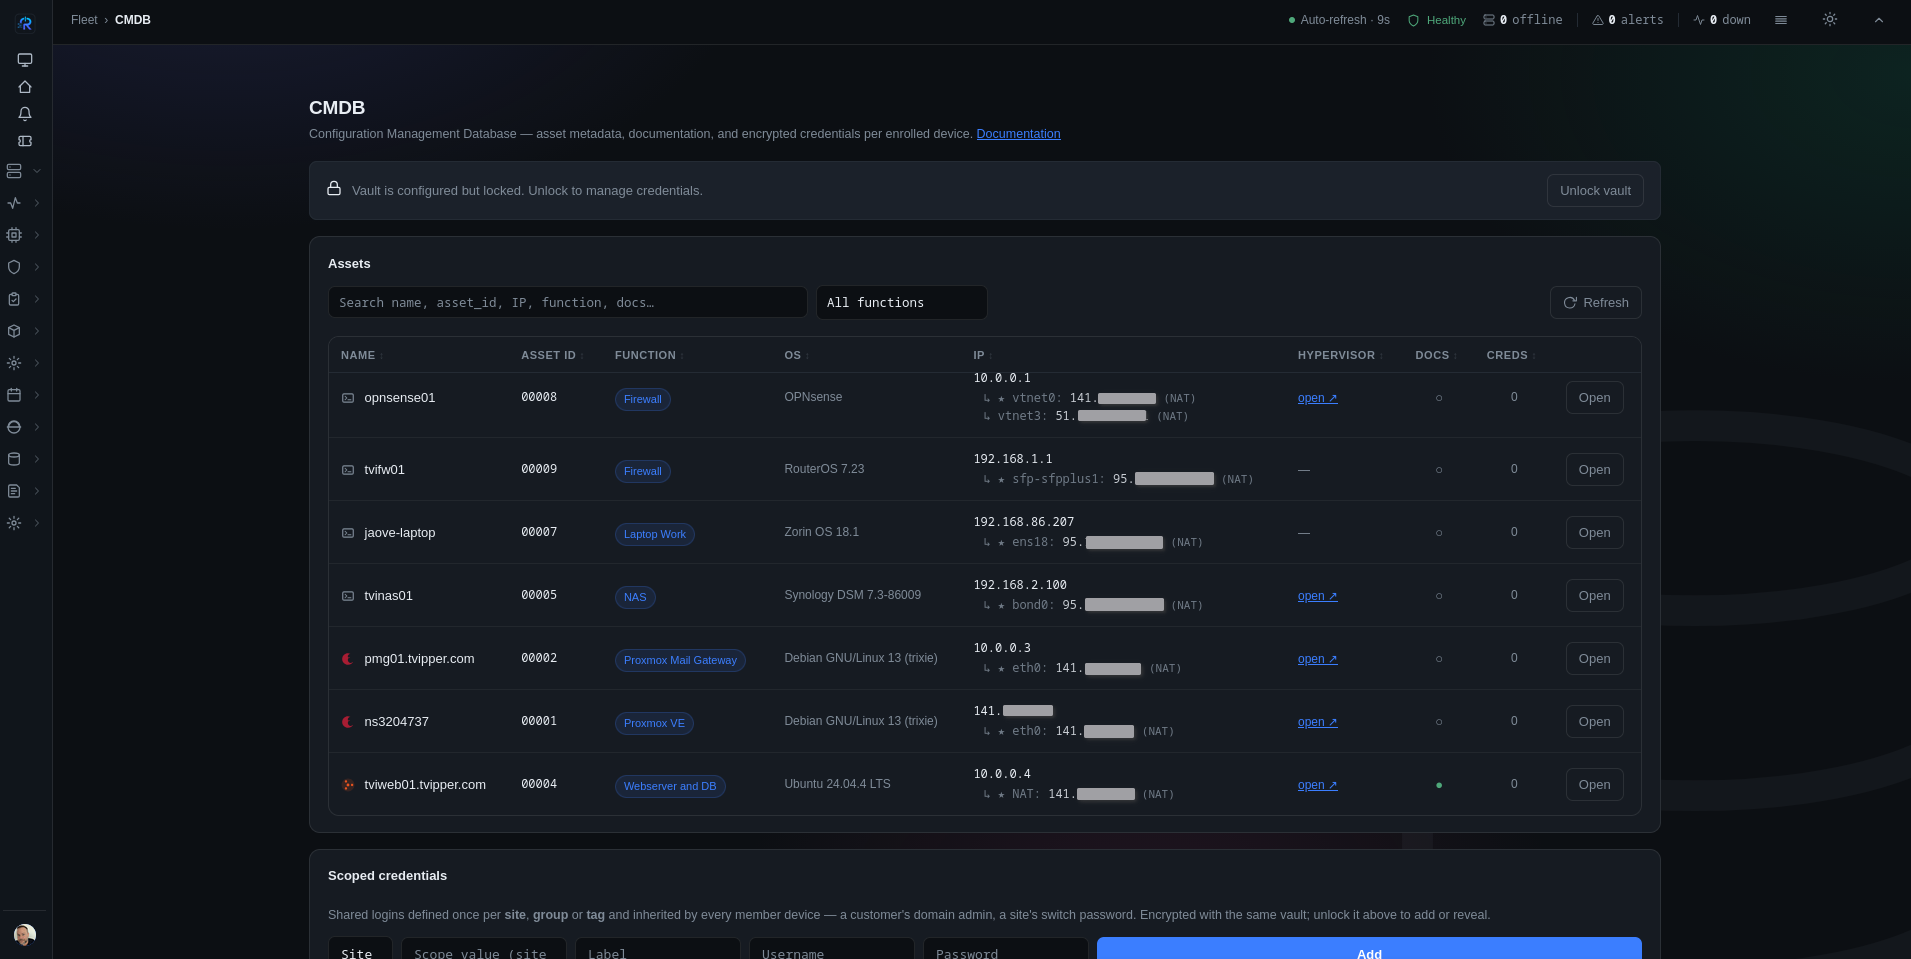
Asset metadata, an encrypted credentials vault with rotation reminders, Markdown docs per asset, a network topology map, and Sites / teams to scope who sees what.
Scan the fleet for exposed secrets and API keys, flag files holding PII, and plant canary tokens / honeyfiles that alert the instant they're read — data-protection tripwires alongside the posture and integrity checks.
Manage host firewalls and fail2ban, issue road-warrior WireGuard access, and drive a network DNS blocker — with a live exposure map of what's reachable from where. Blocklist changes are edge-triggered and audited.
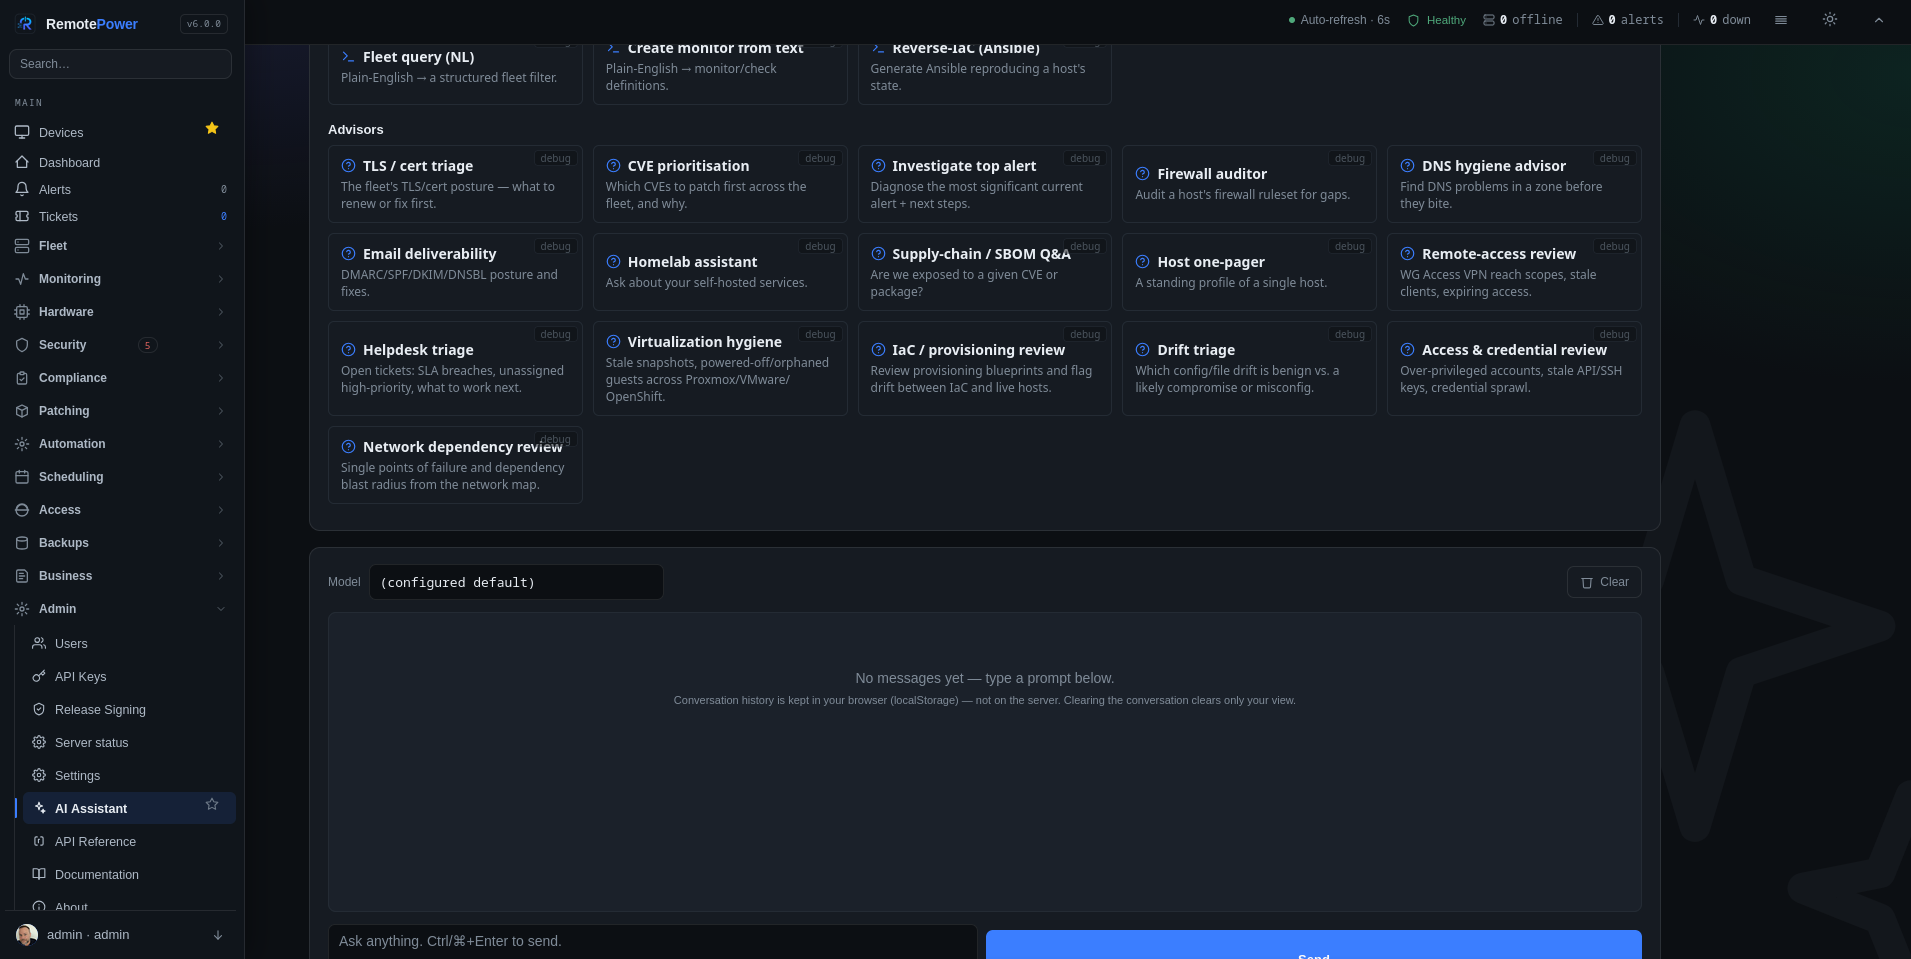
The assistant retrieves facts from your own hosts, CVEs, CMDB and runbooks and cites them — so answers reference your infrastructure, not generic advice.
One click on a Needs-Attention item runs a diagnosis and proposes a fix — across ~20 kinds: disks, CVEs, drift, failed units, AV posture, hardware, and more. Agentic log diagnosis sweeps a host's logs and follows the evidence under hard token budgets, with secrets redacted and a visible evidence trail; opt-in auto-remediation re-verifies and backs off. Security-sensitive ones never propose a blind destructive command.
When an event fires, auto-run a saved script or notify a destination — e.g. restart a service the moment it goes down. Plus a plain-English cron builder and RAG-aware runbook drafts.
Connect an MCP client like Claude Desktop to ask about your fleet in plain language — 16 read tools over alerts, devices, journals, services, containers, CVEs, drift and more, plus 5 guarded write actions. Reads need only a viewer-role key; the writes are a fixed, pre-saved set and every one is audited with the AI host and the prompt that triggered it.
An alerts inbox with a routing matrix, on-call & escalation, Slack / Discord / Teams / ntfy / email / PagerDuty, inbound webhooks & syslog, SNMP, and Prometheus metrics.
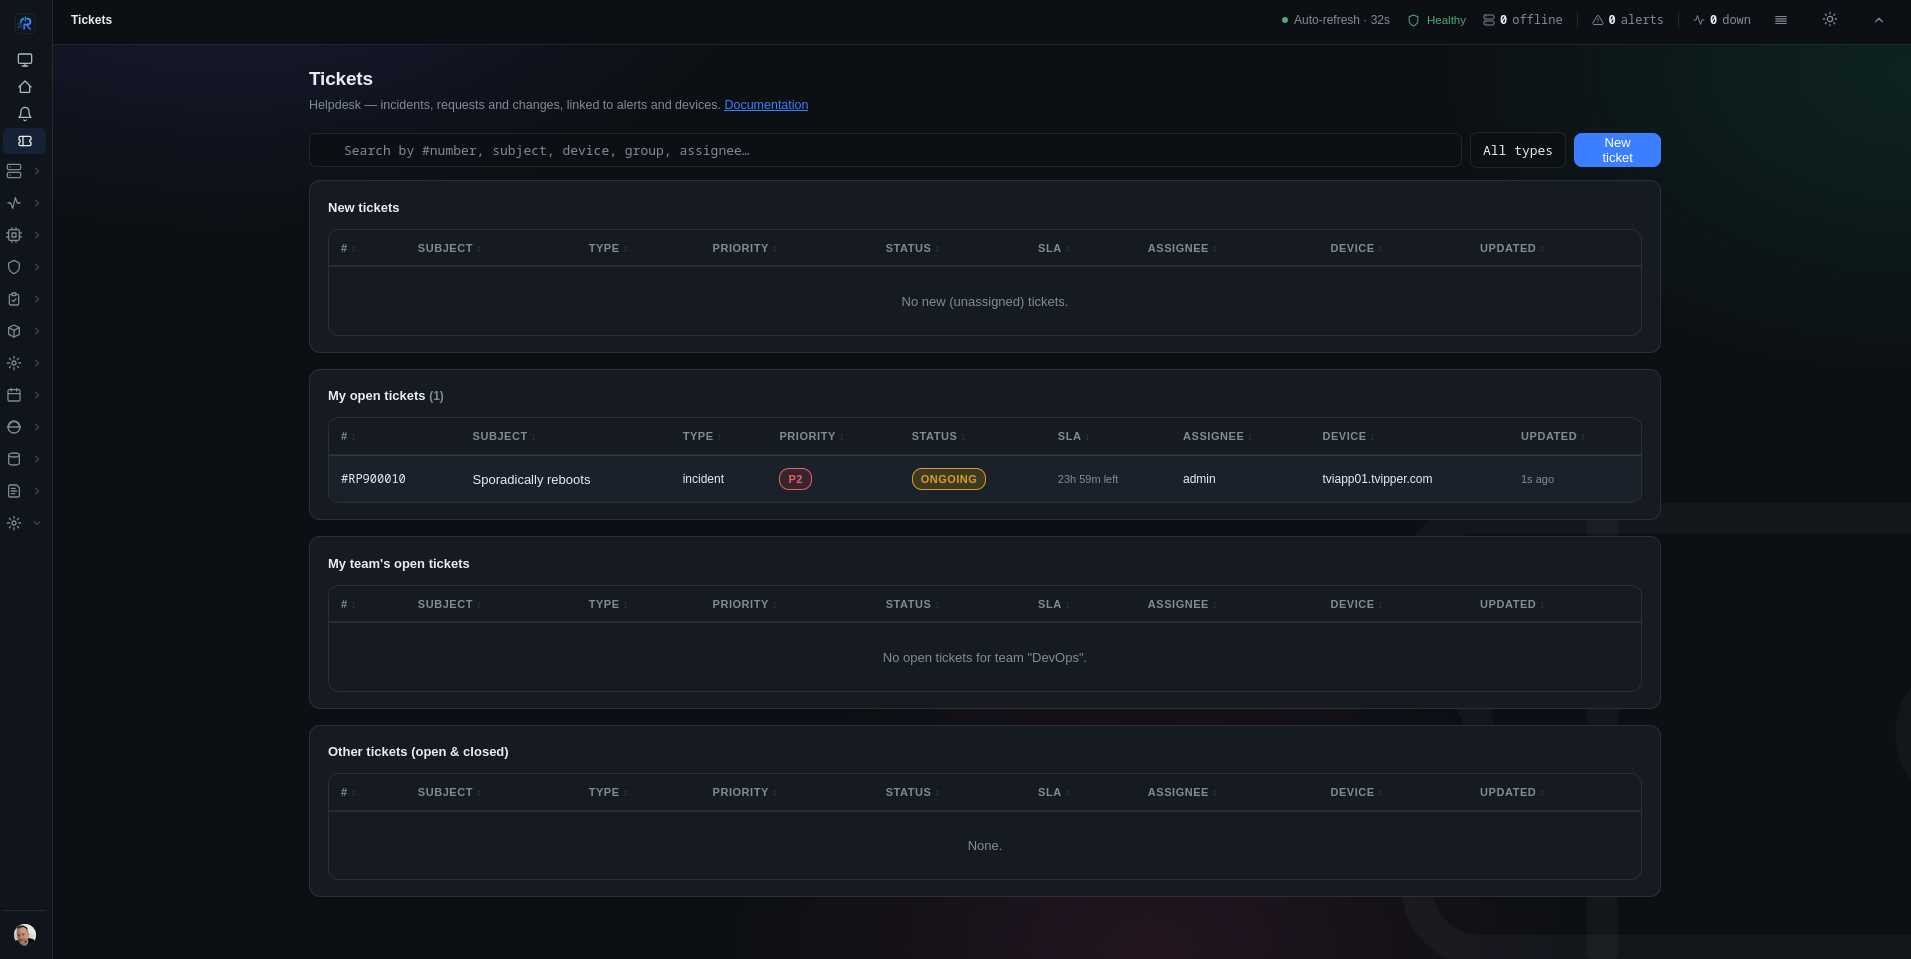
A built-in ticket system — open from an alert, assign, comment, log hours and track SLA — with email intake, auto-heal linkage so a resolved alert can close its ticket, and full audit history. No second tool to run.
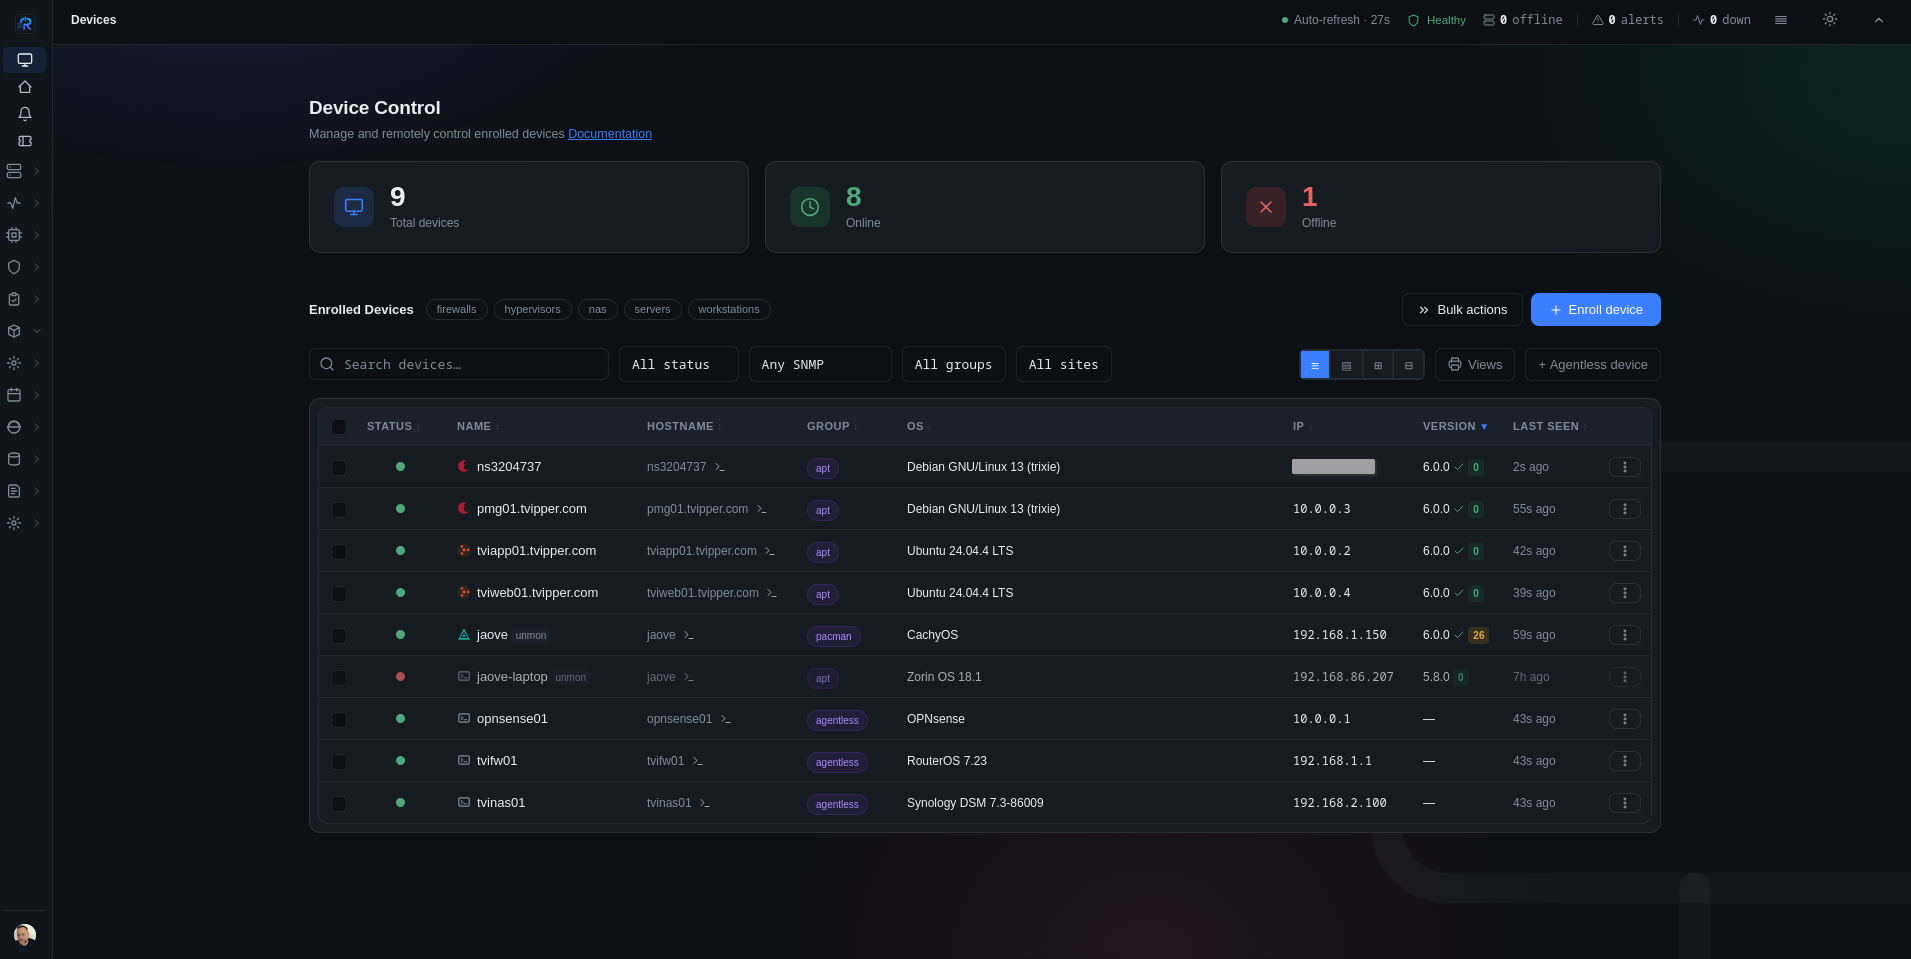
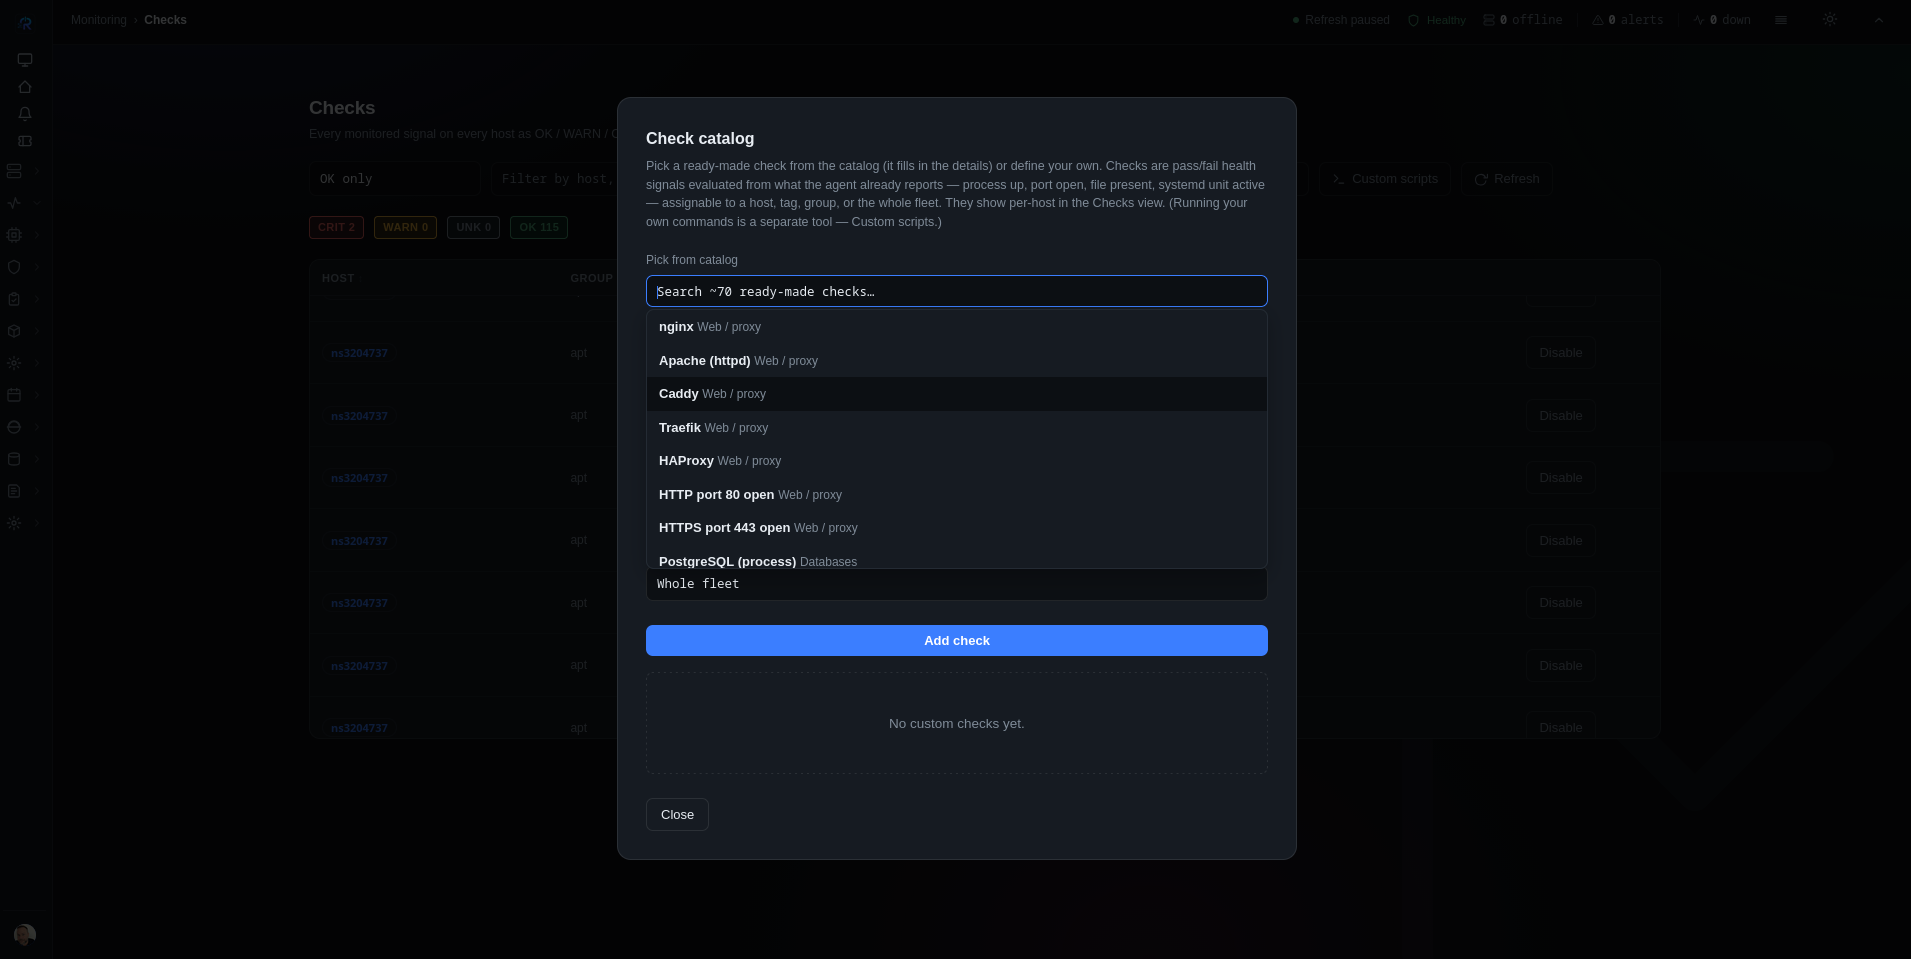
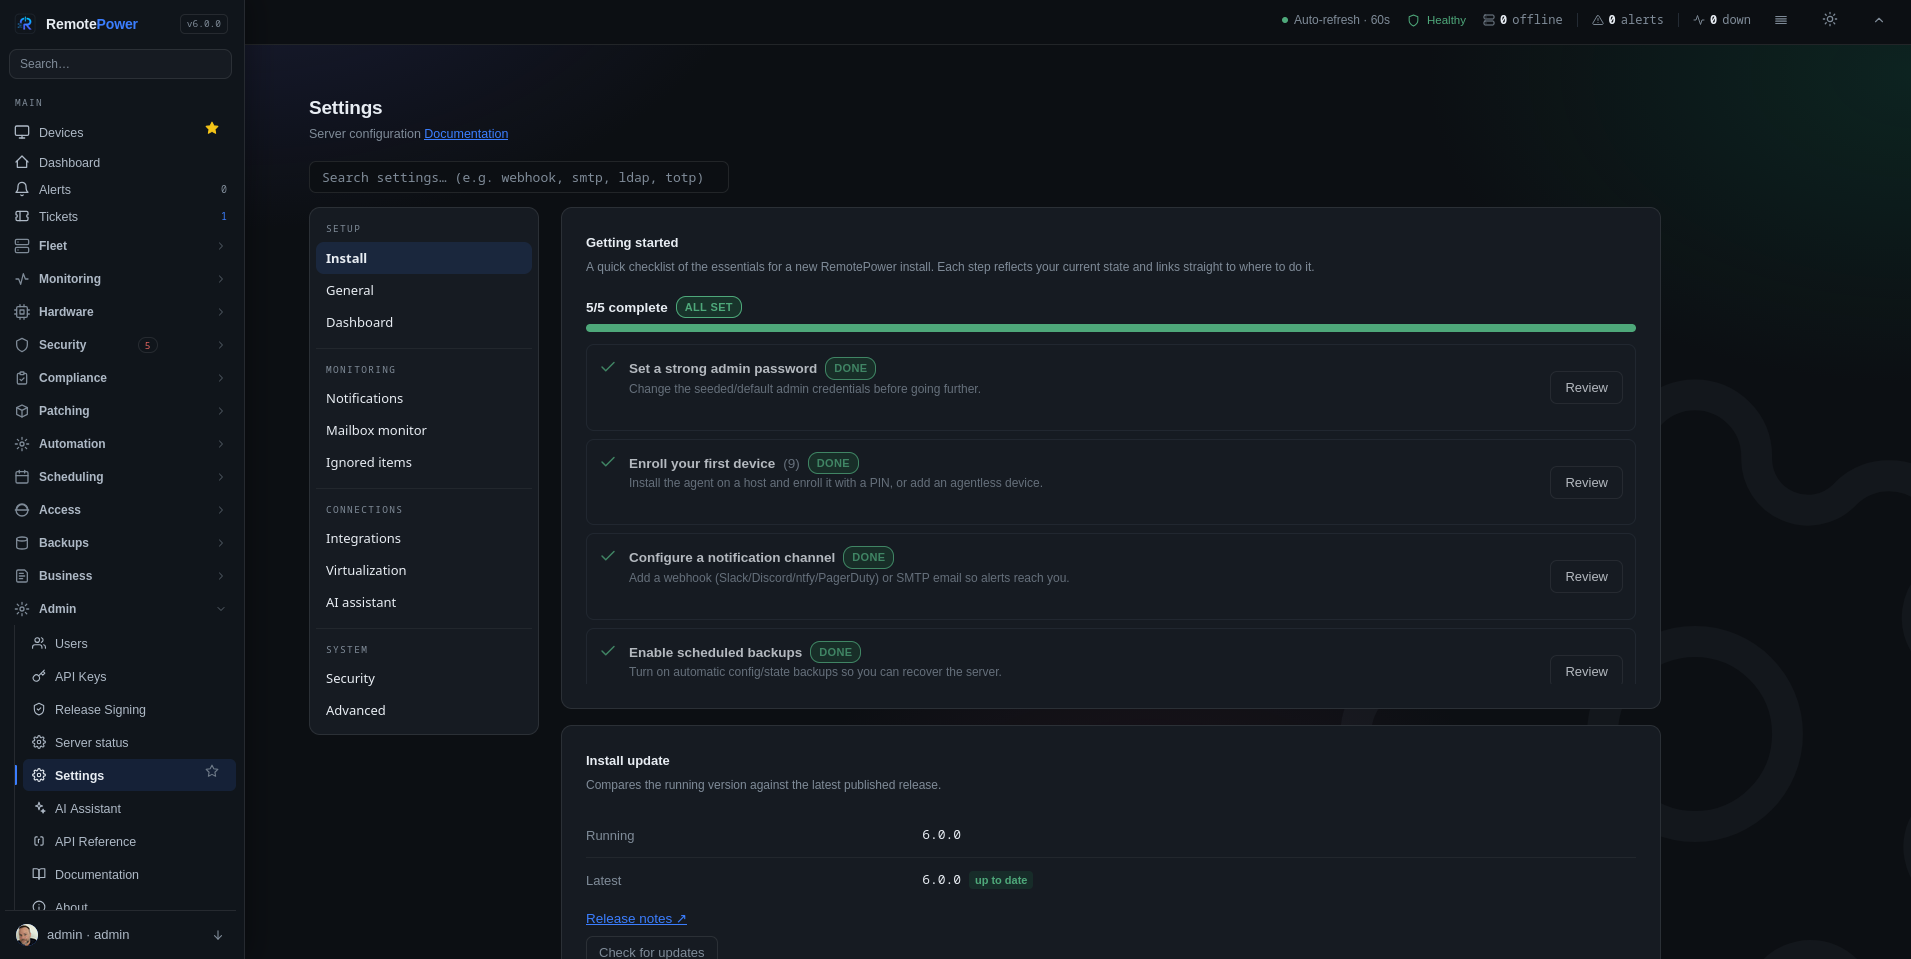
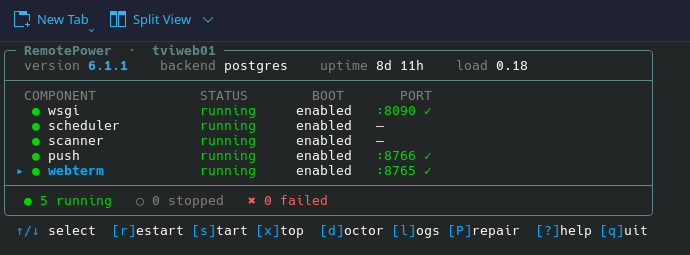
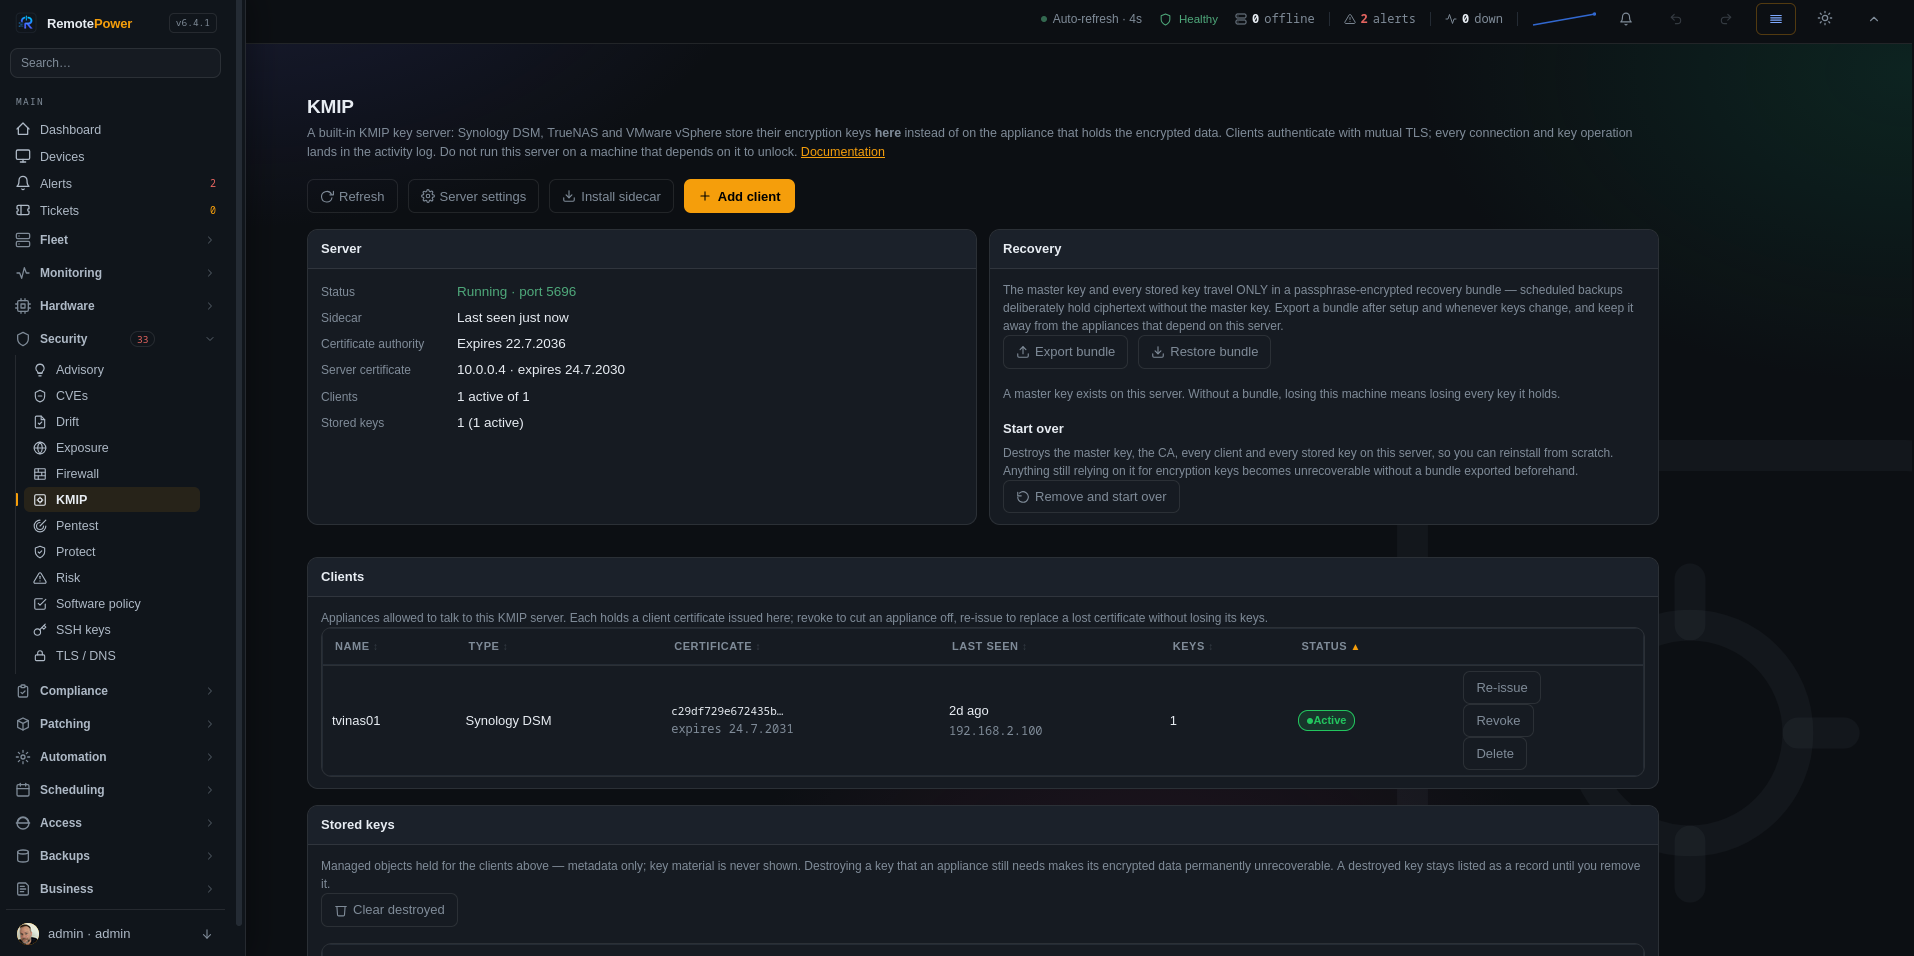
A few corners of the dashboard. Everything below is one self-hosted app — no tabs sprawling across a dozen tools.
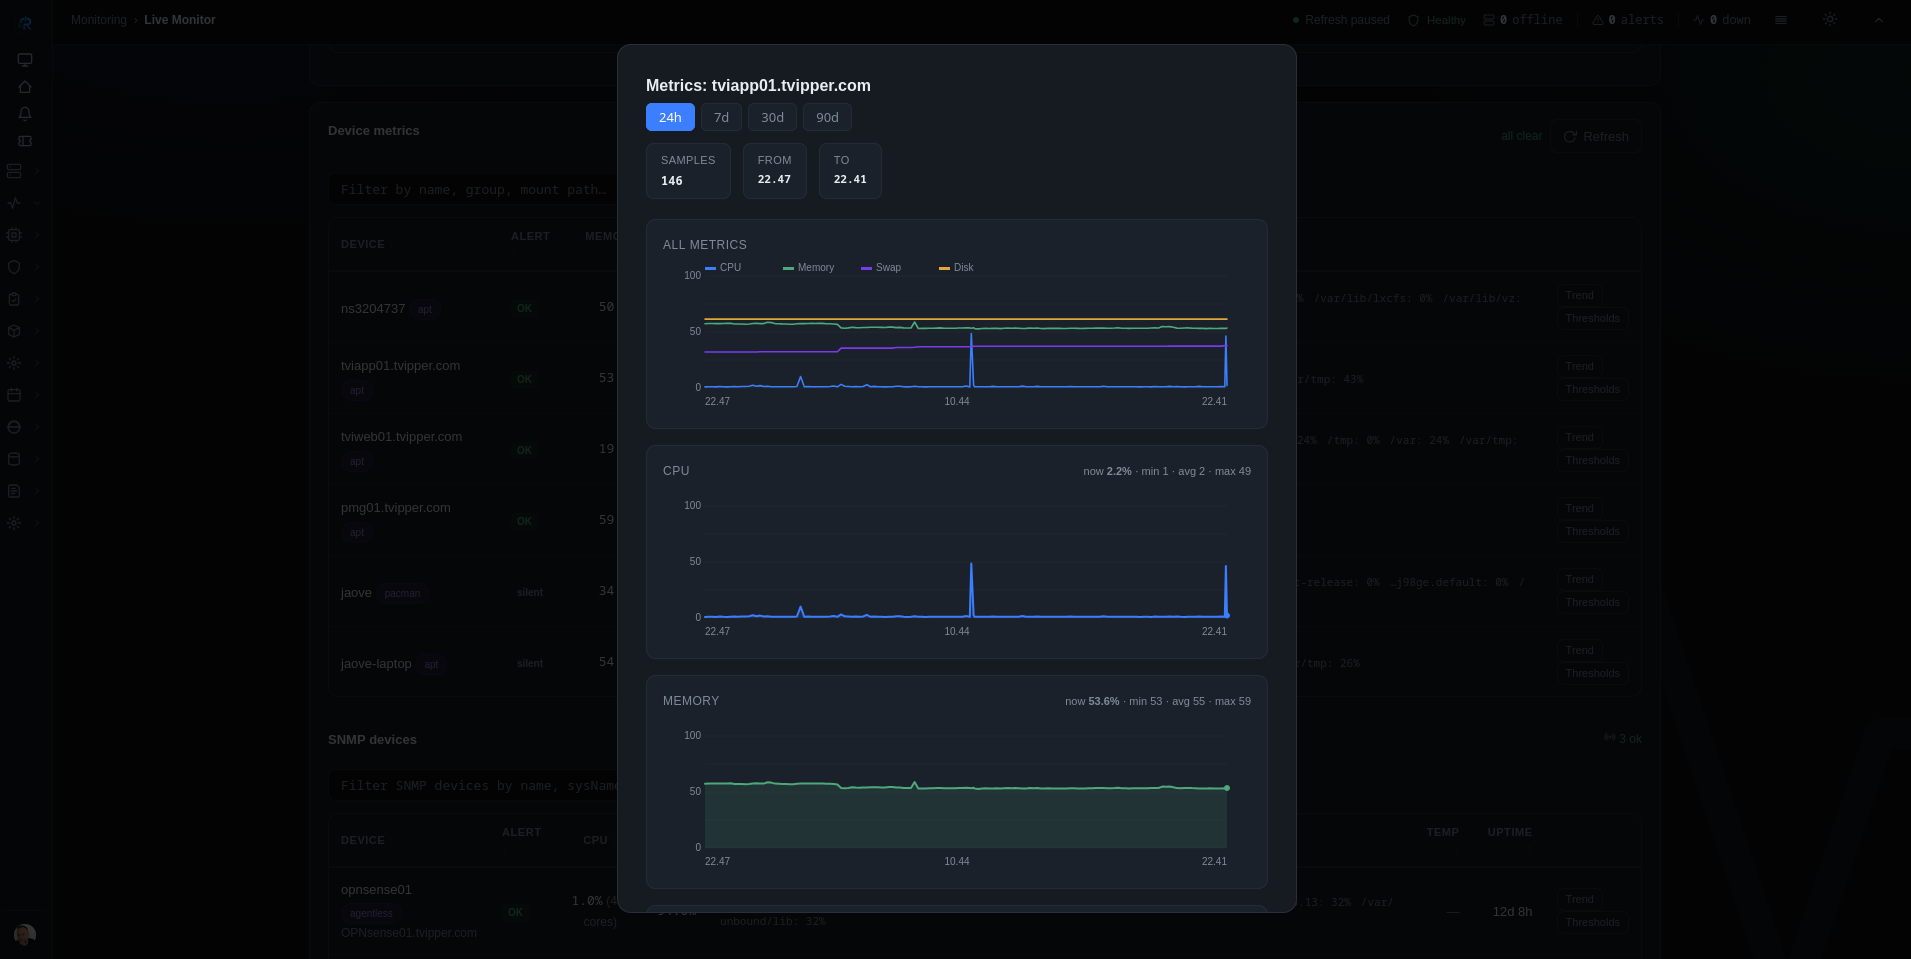
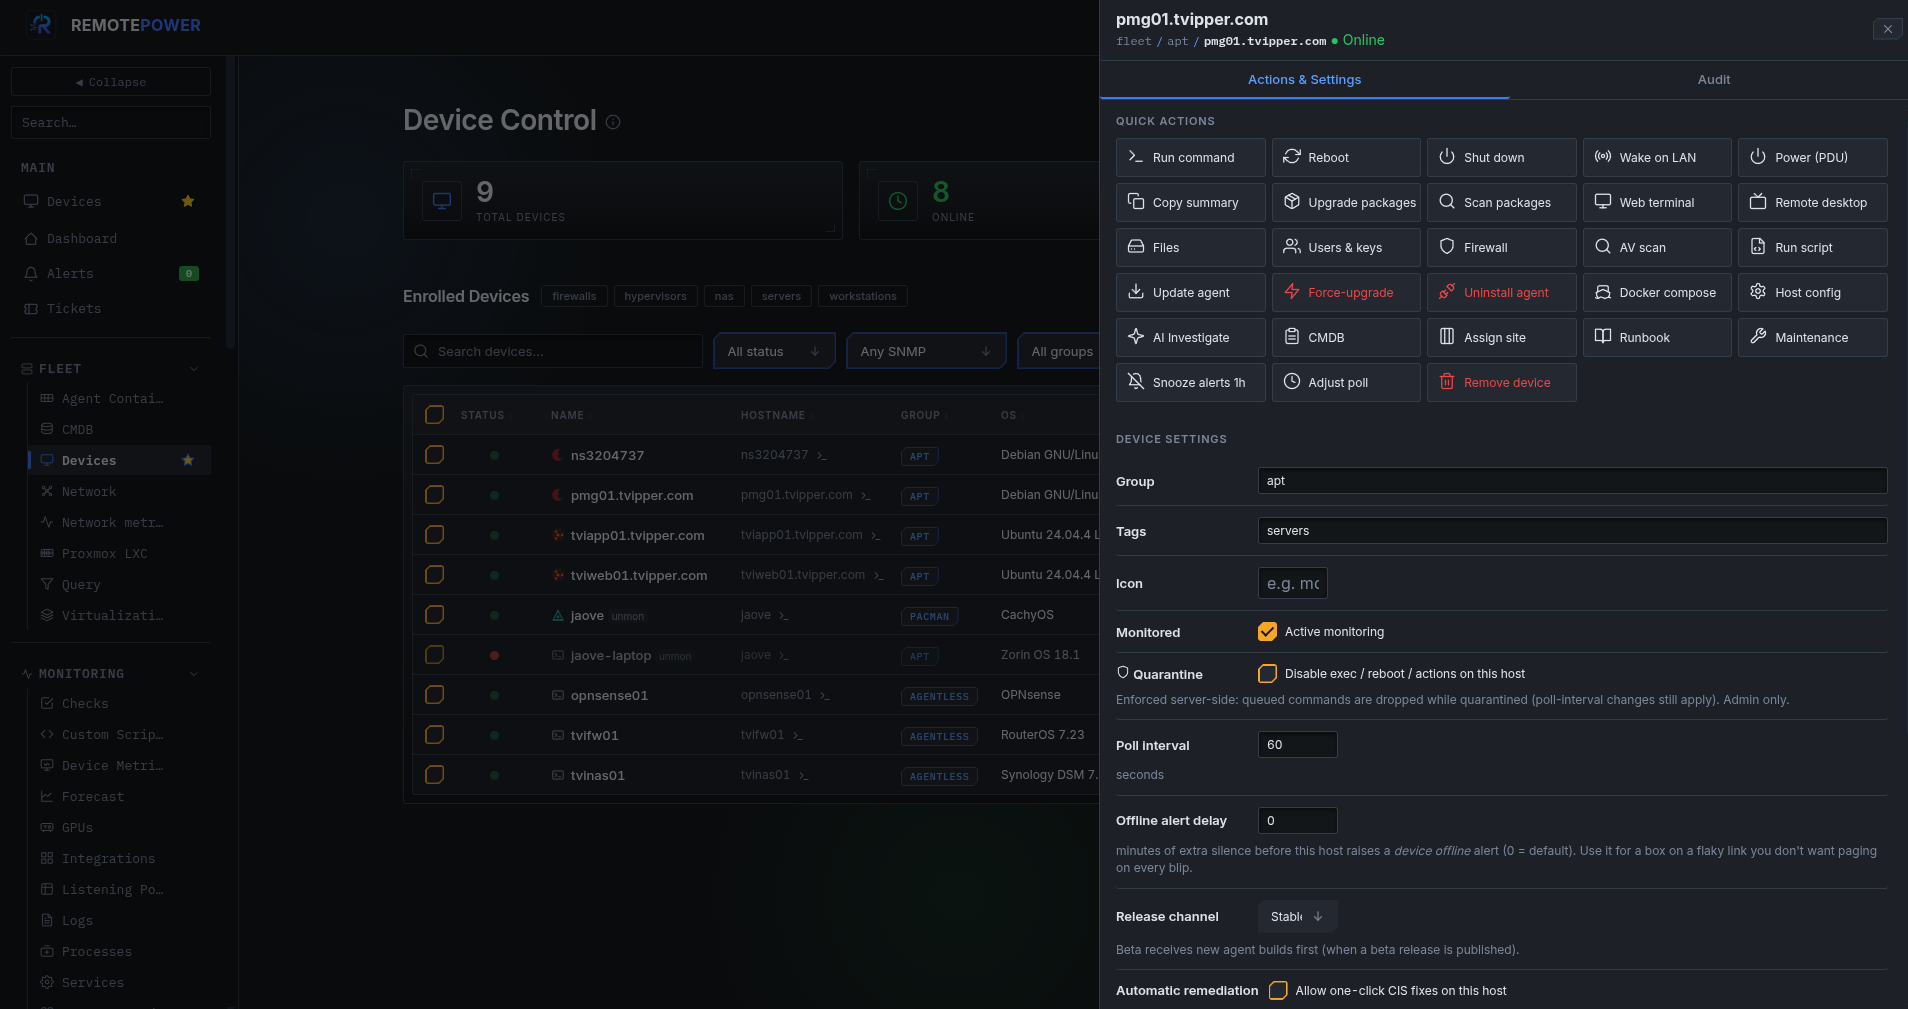
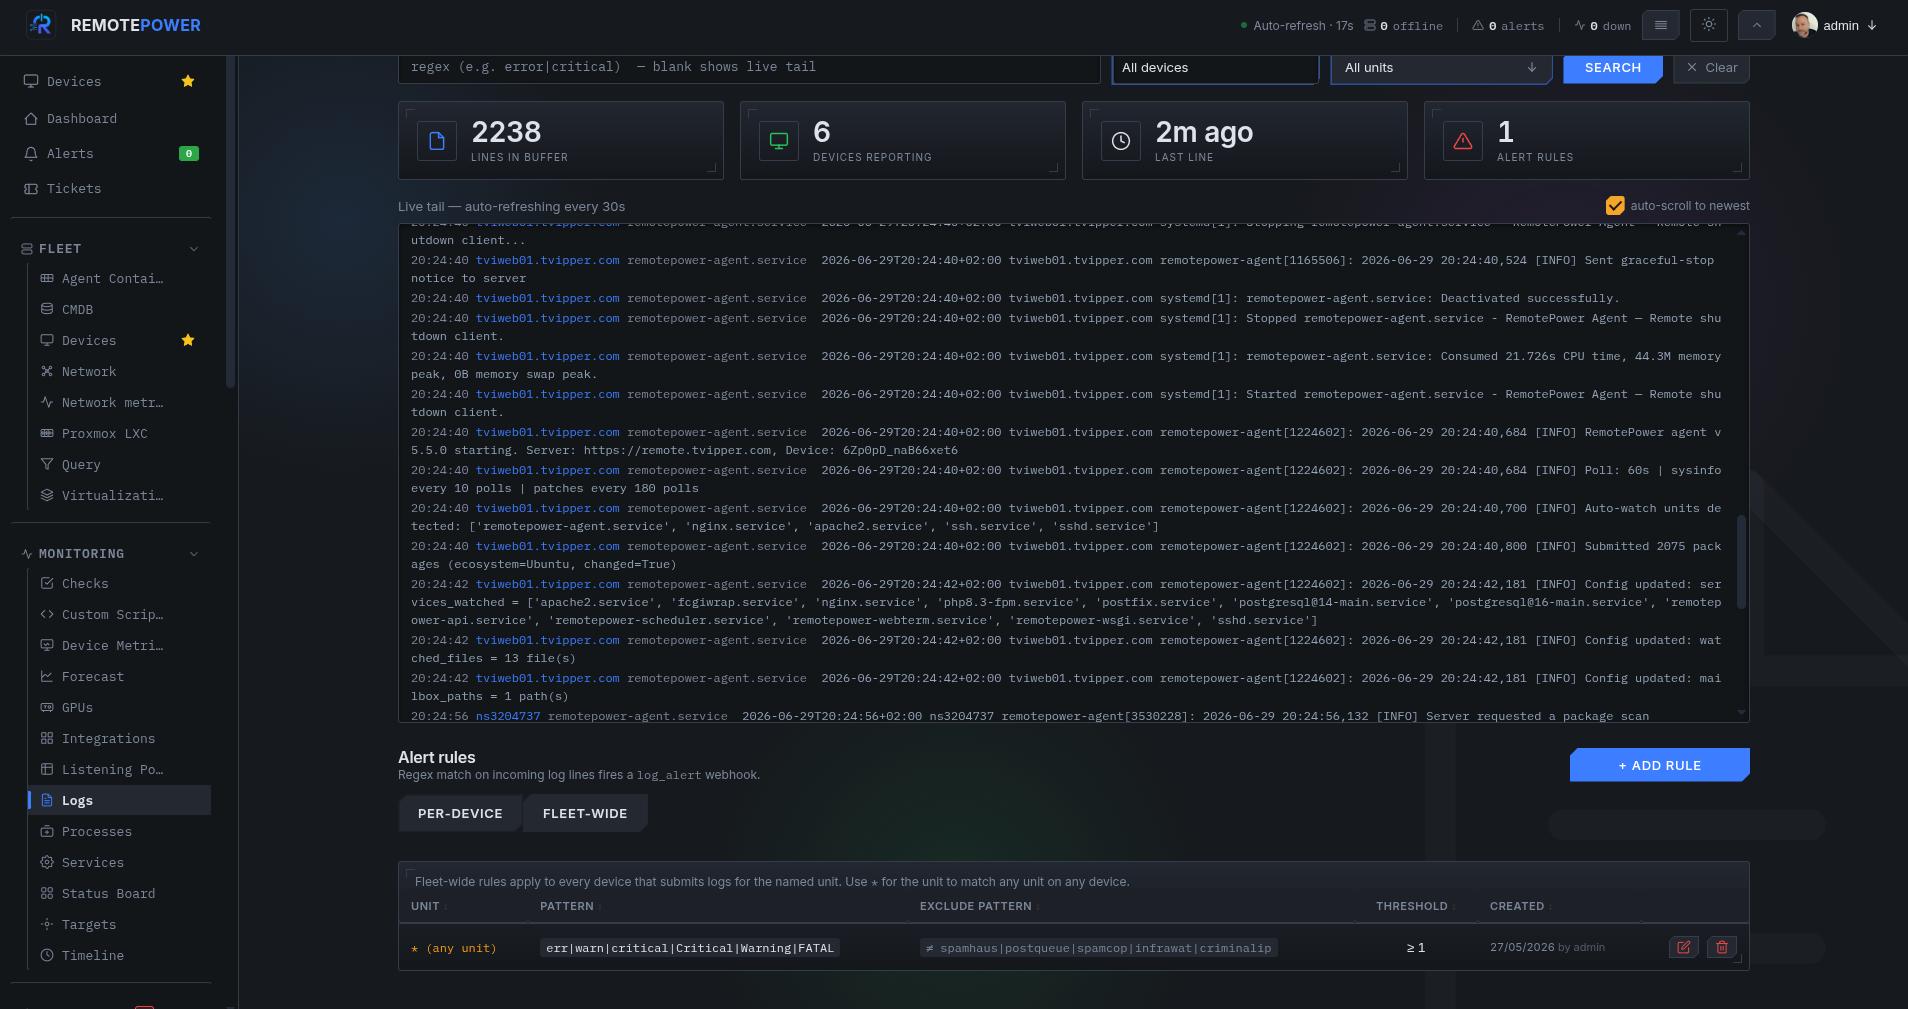
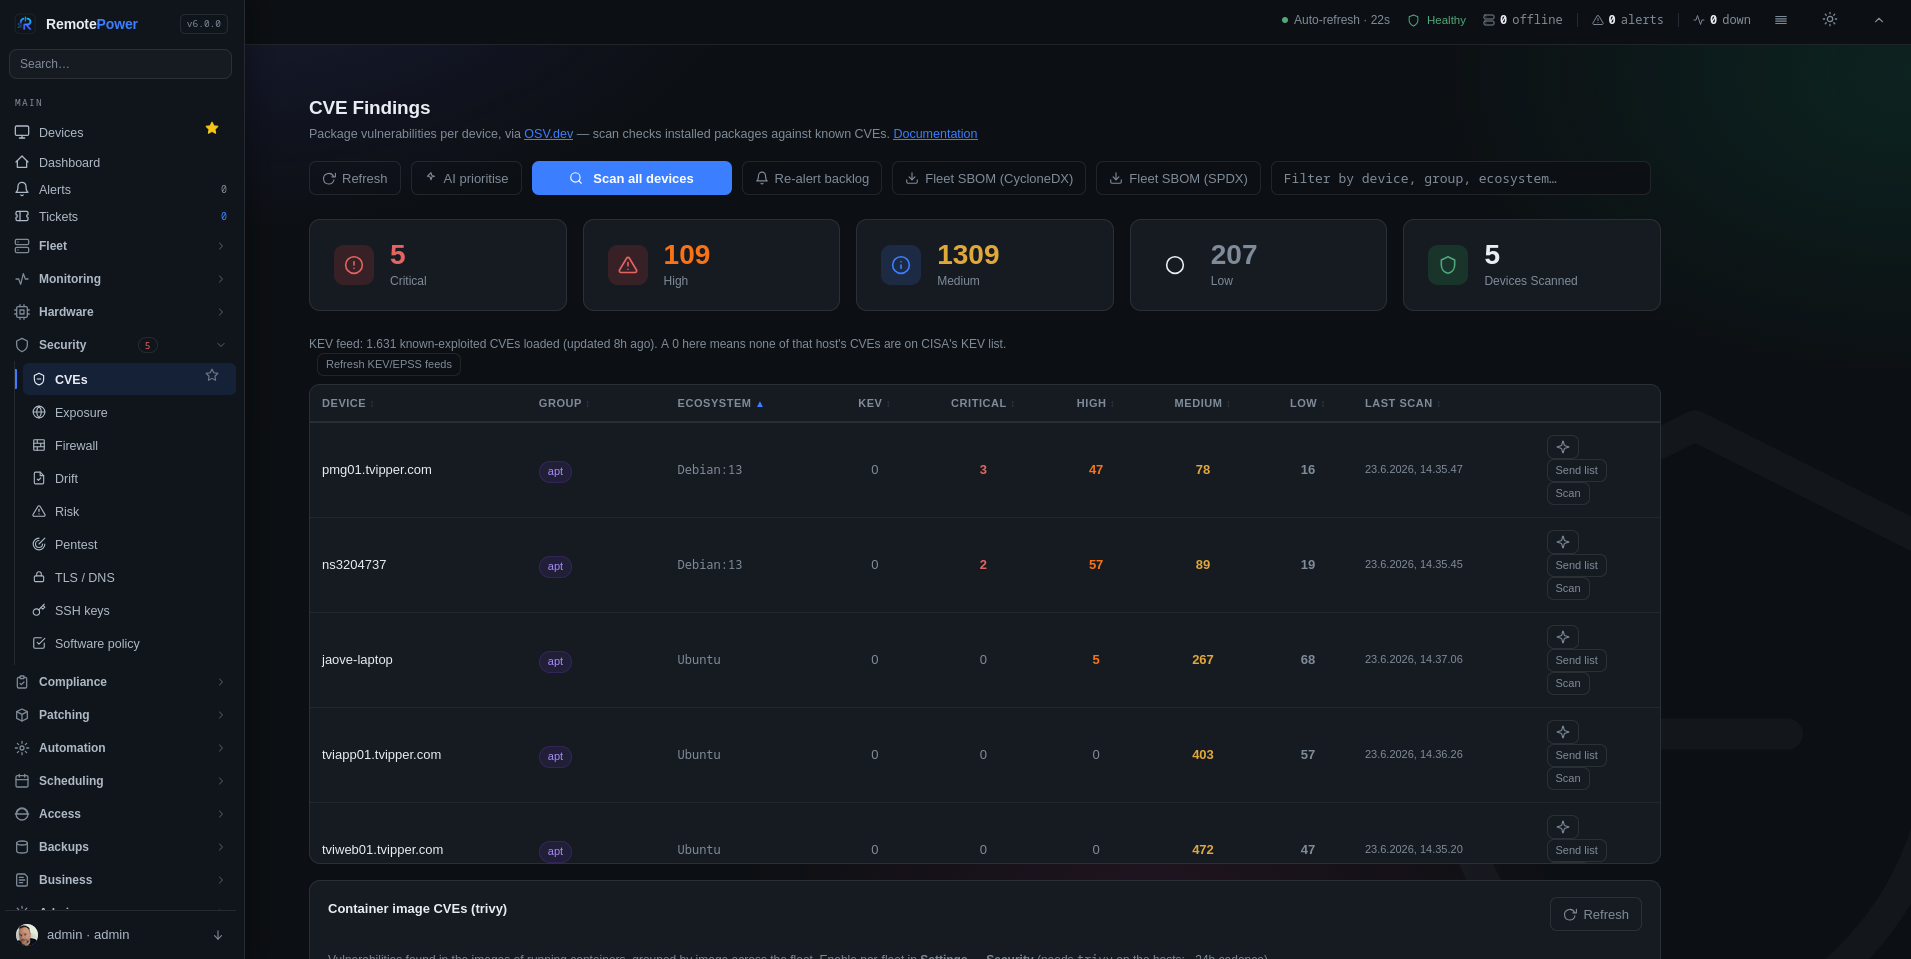
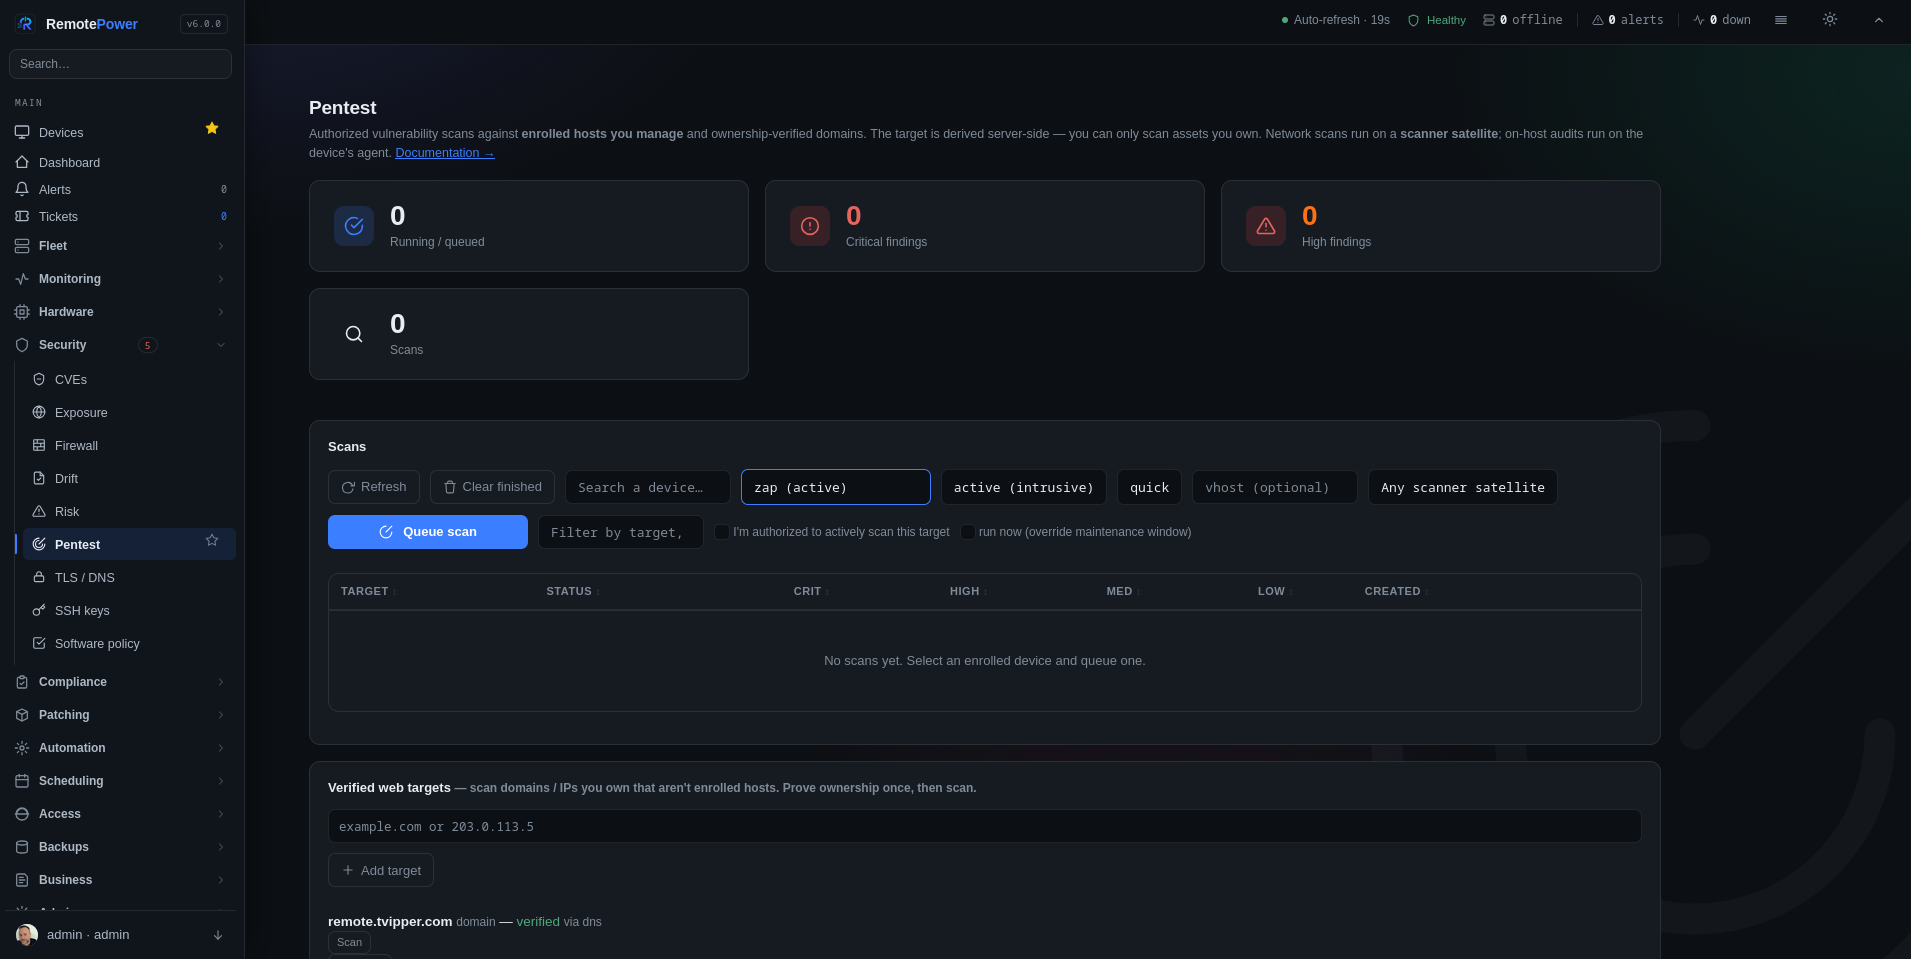
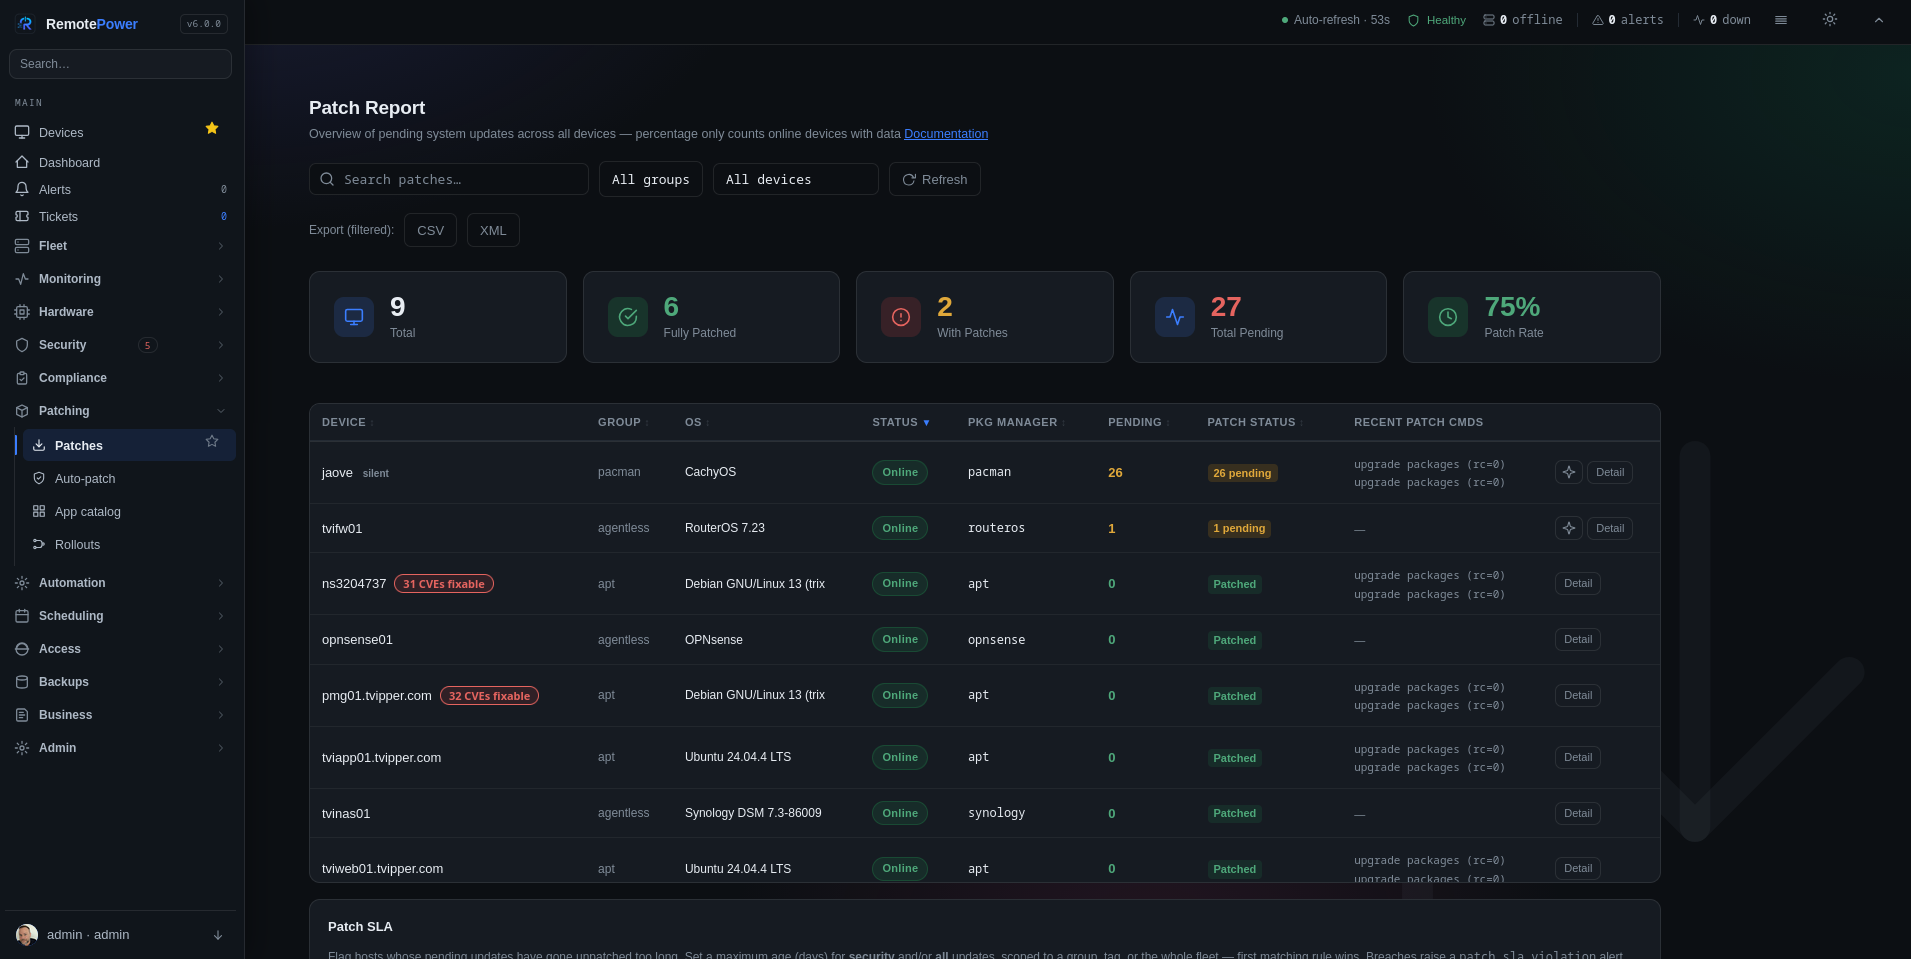
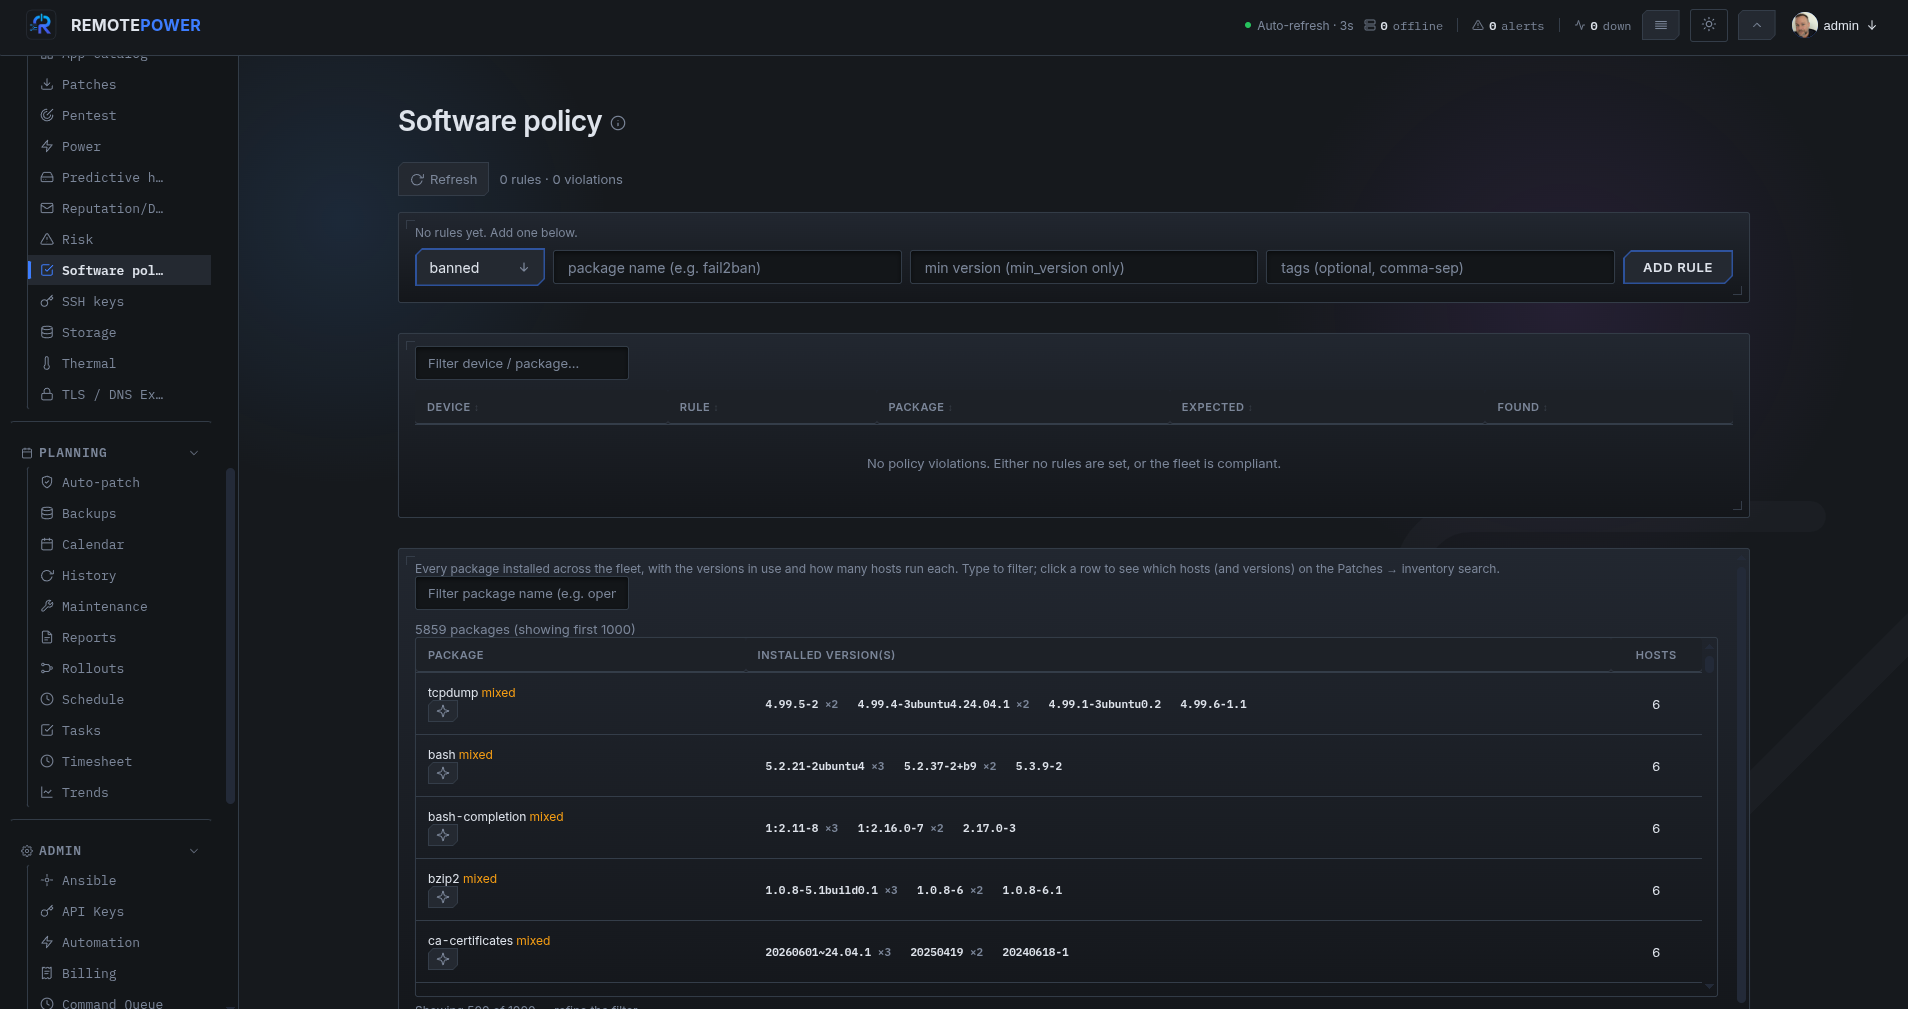
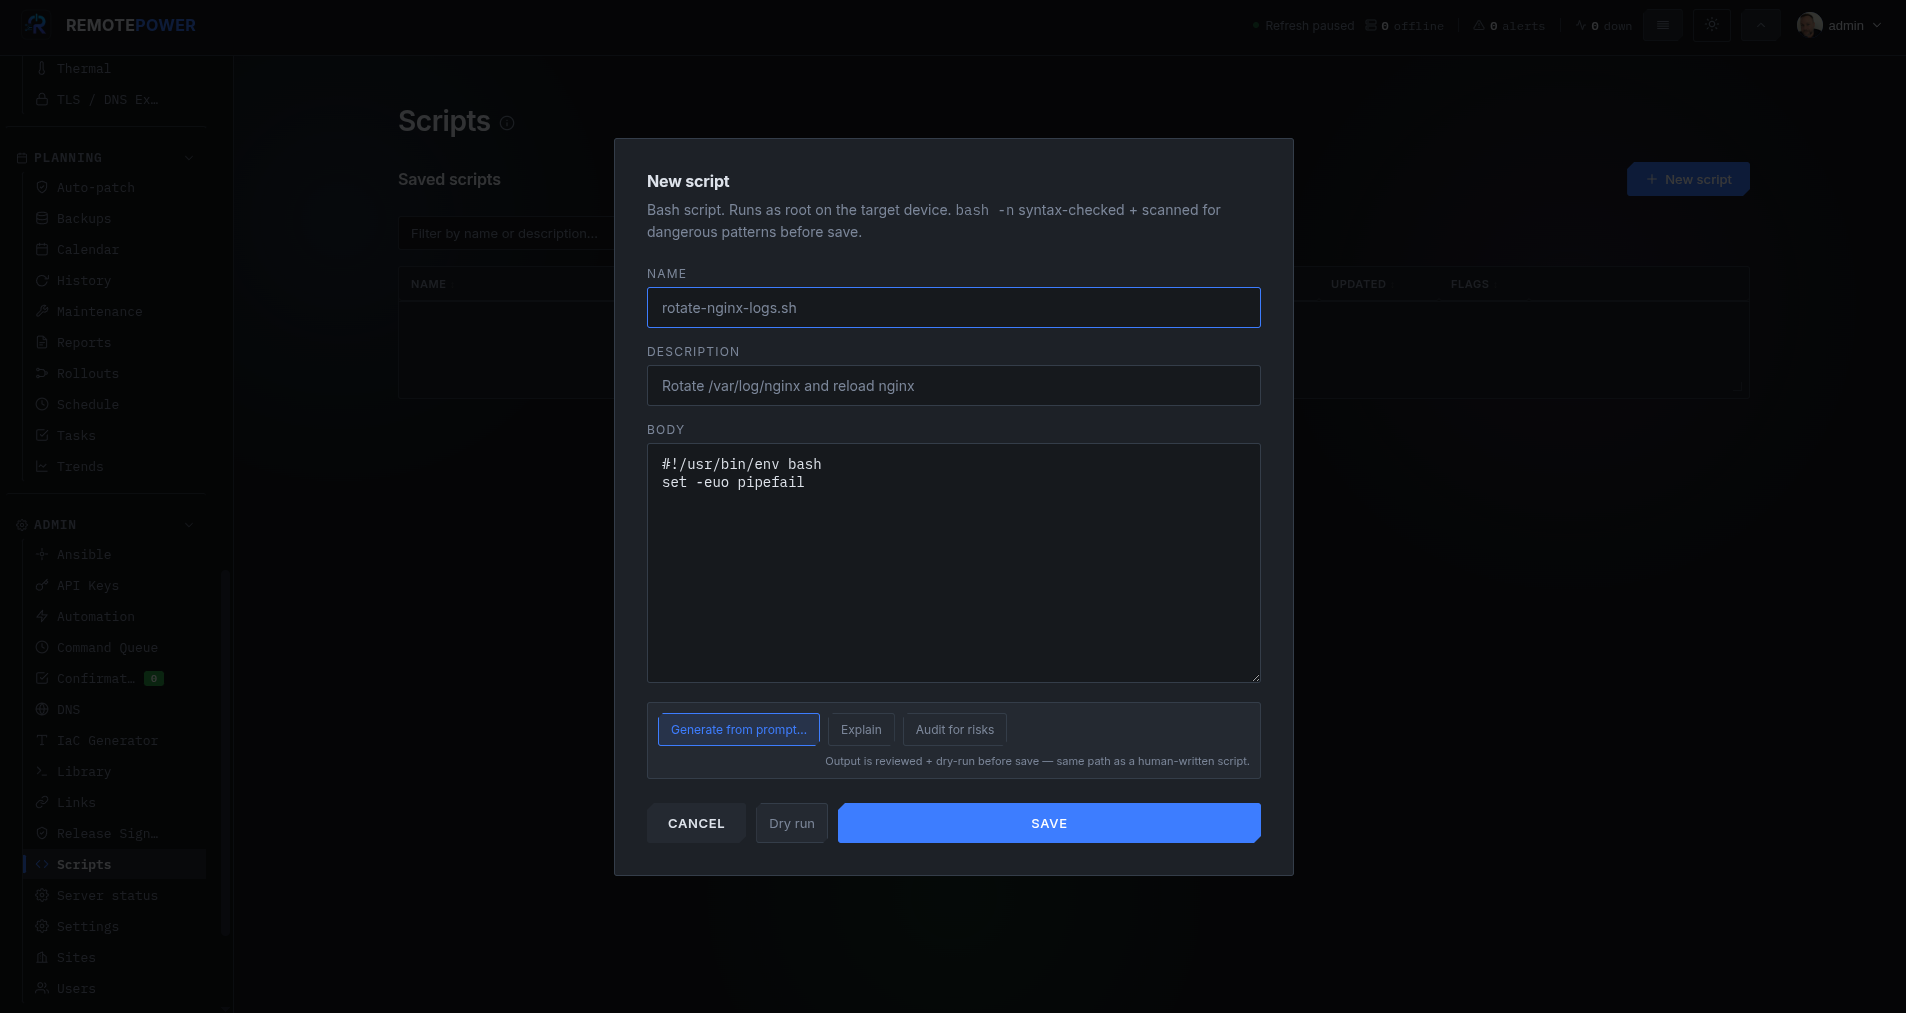
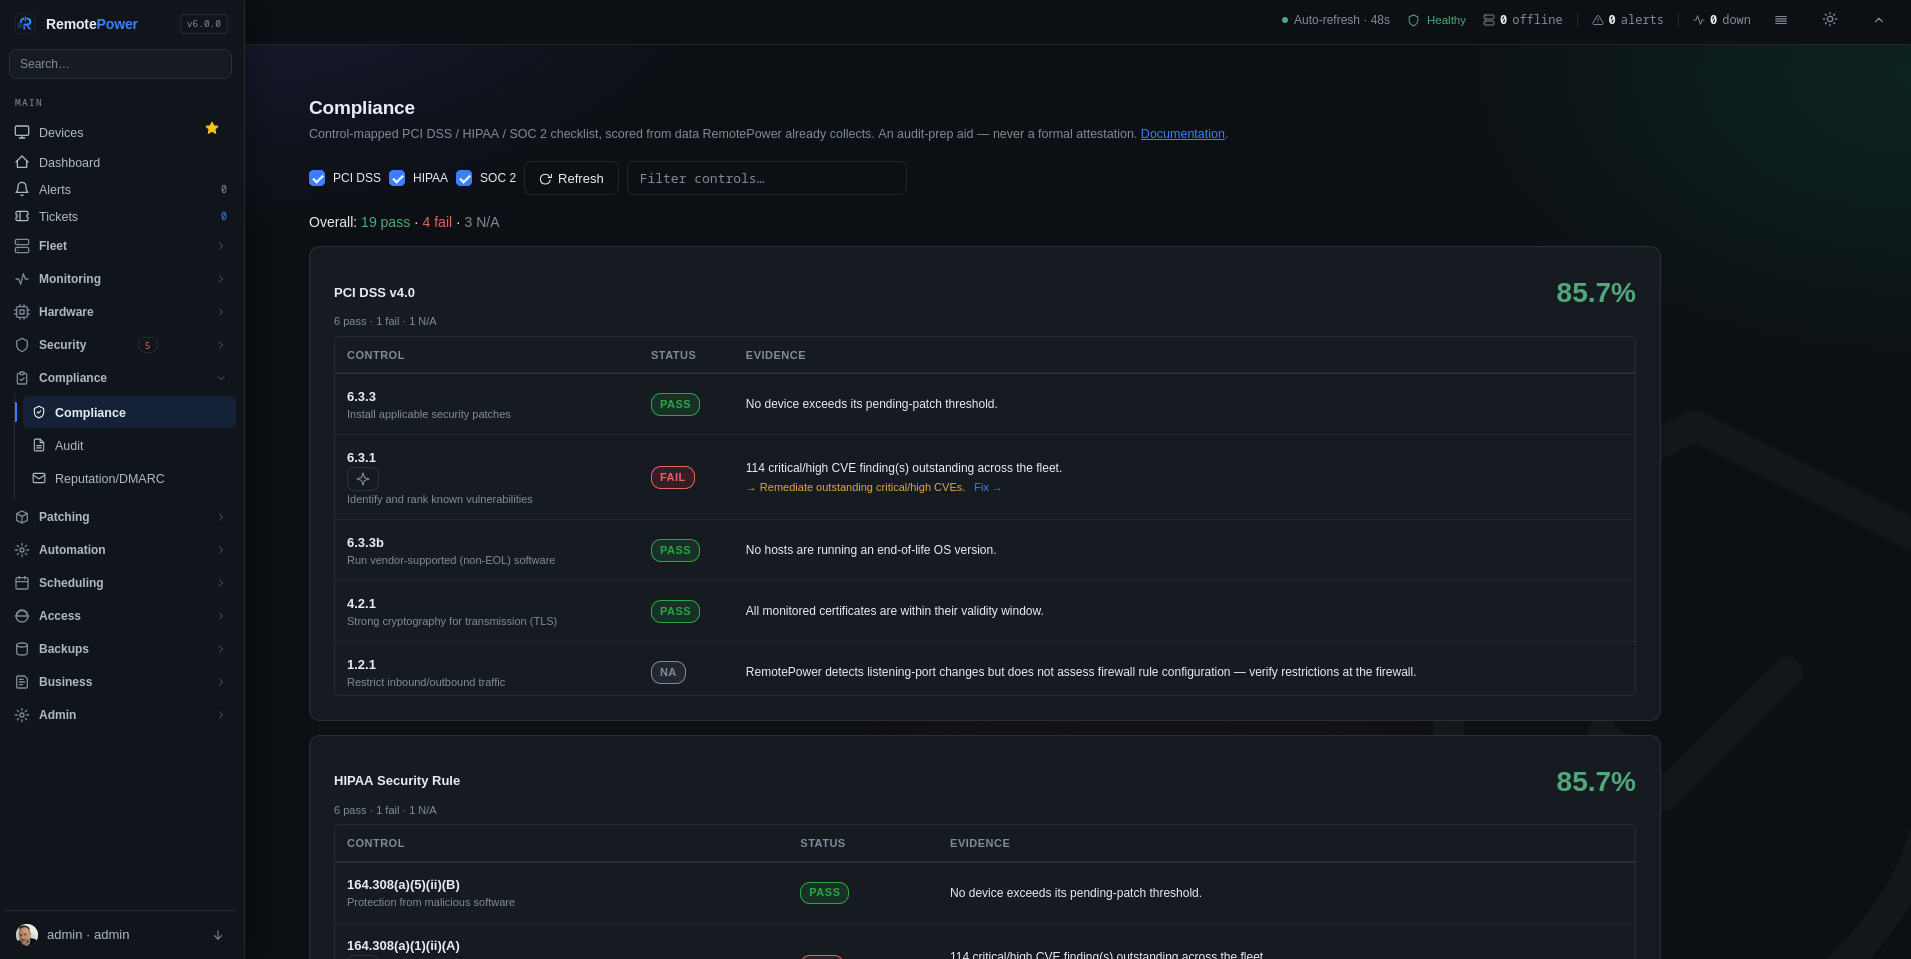
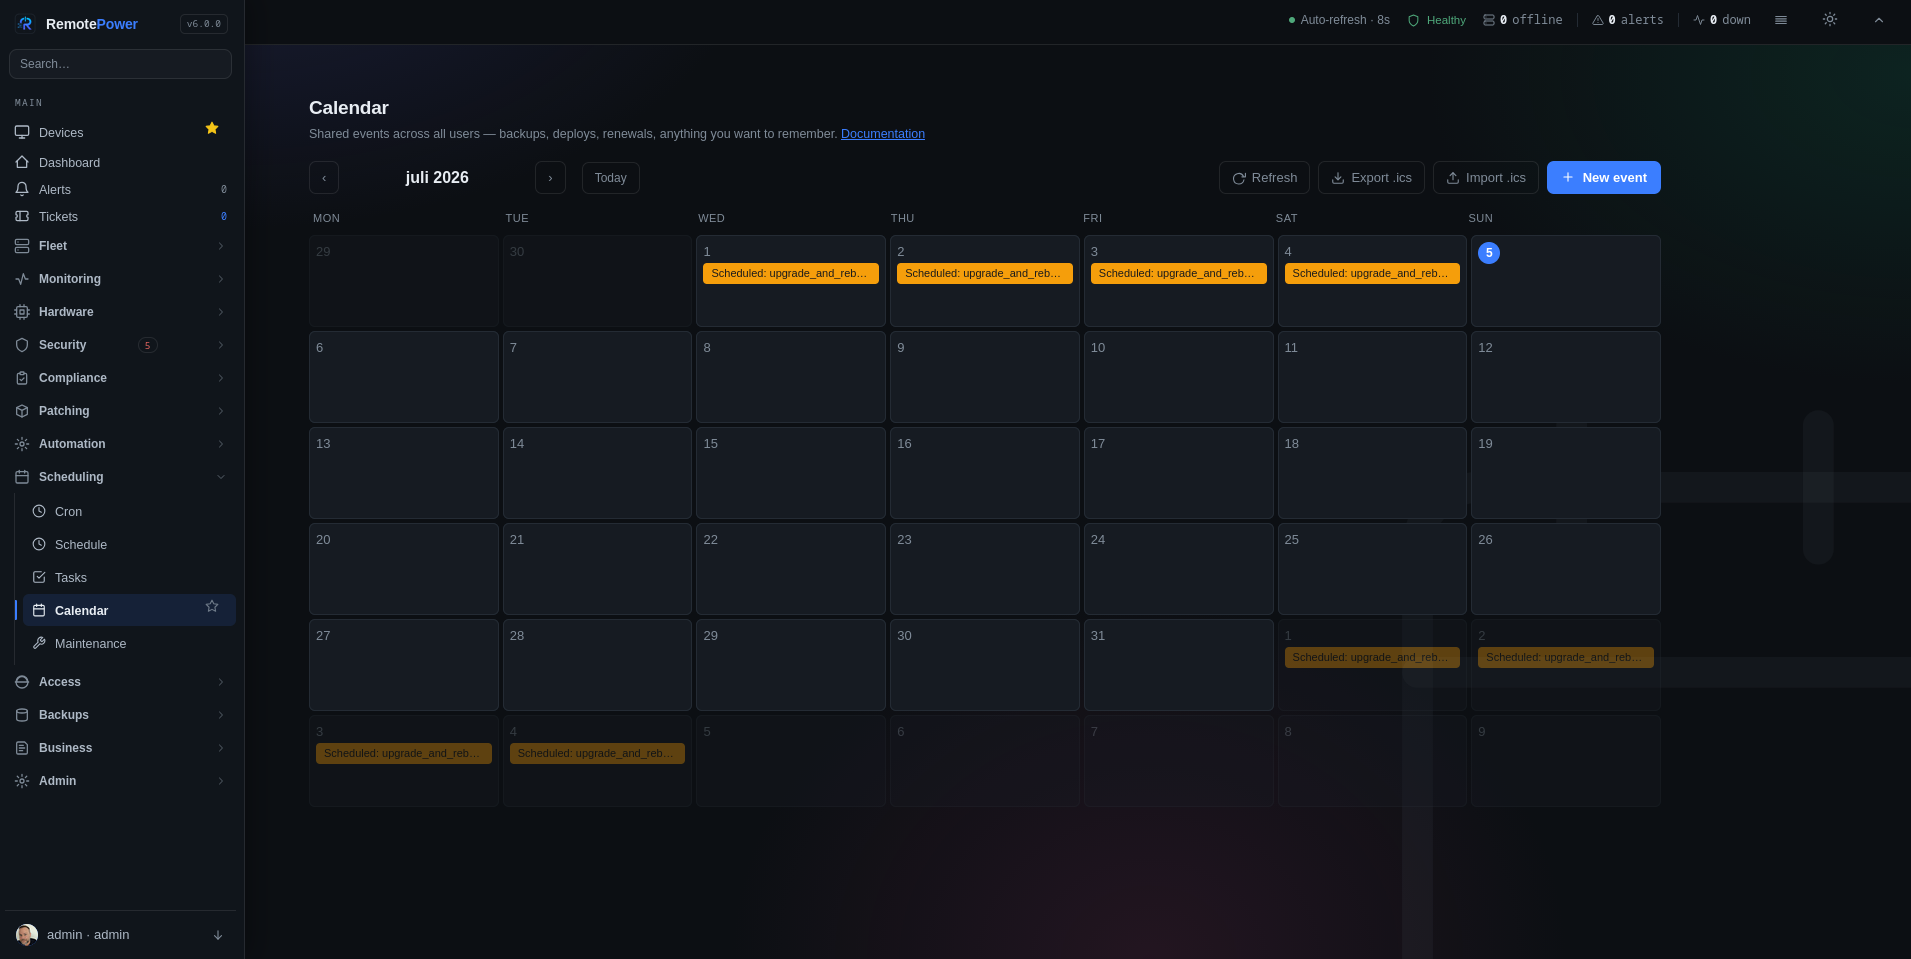
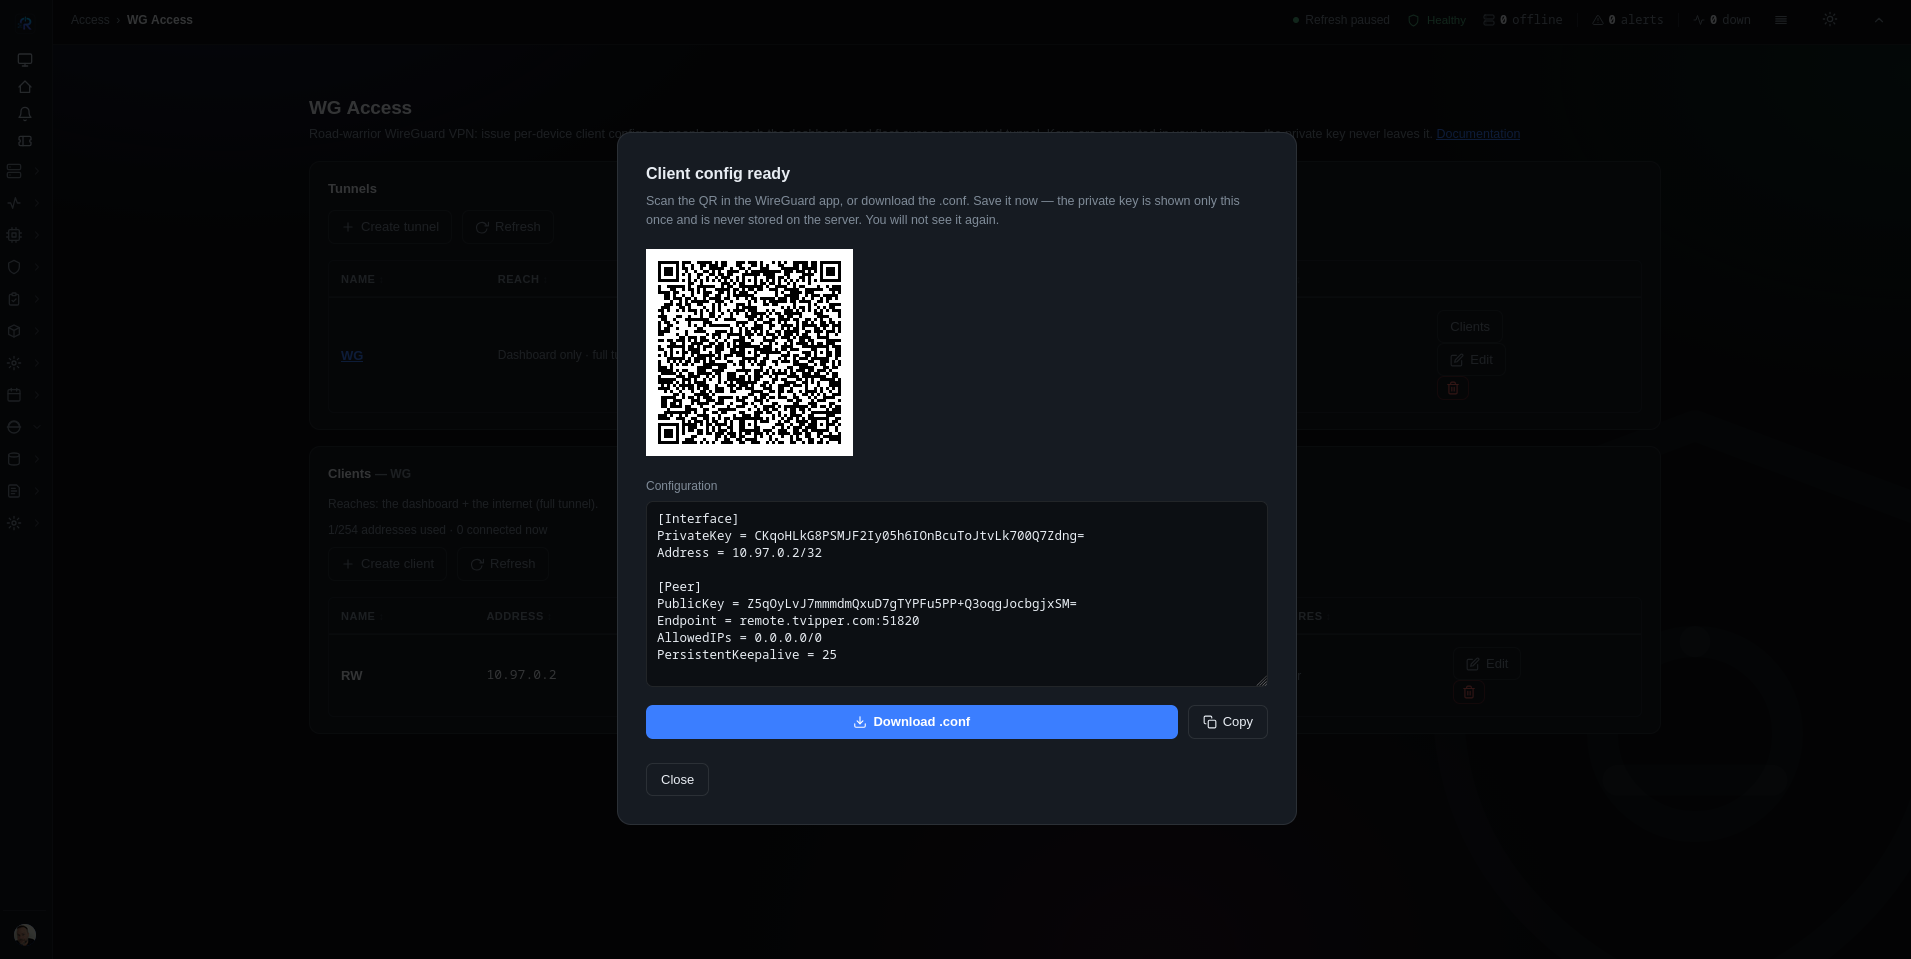
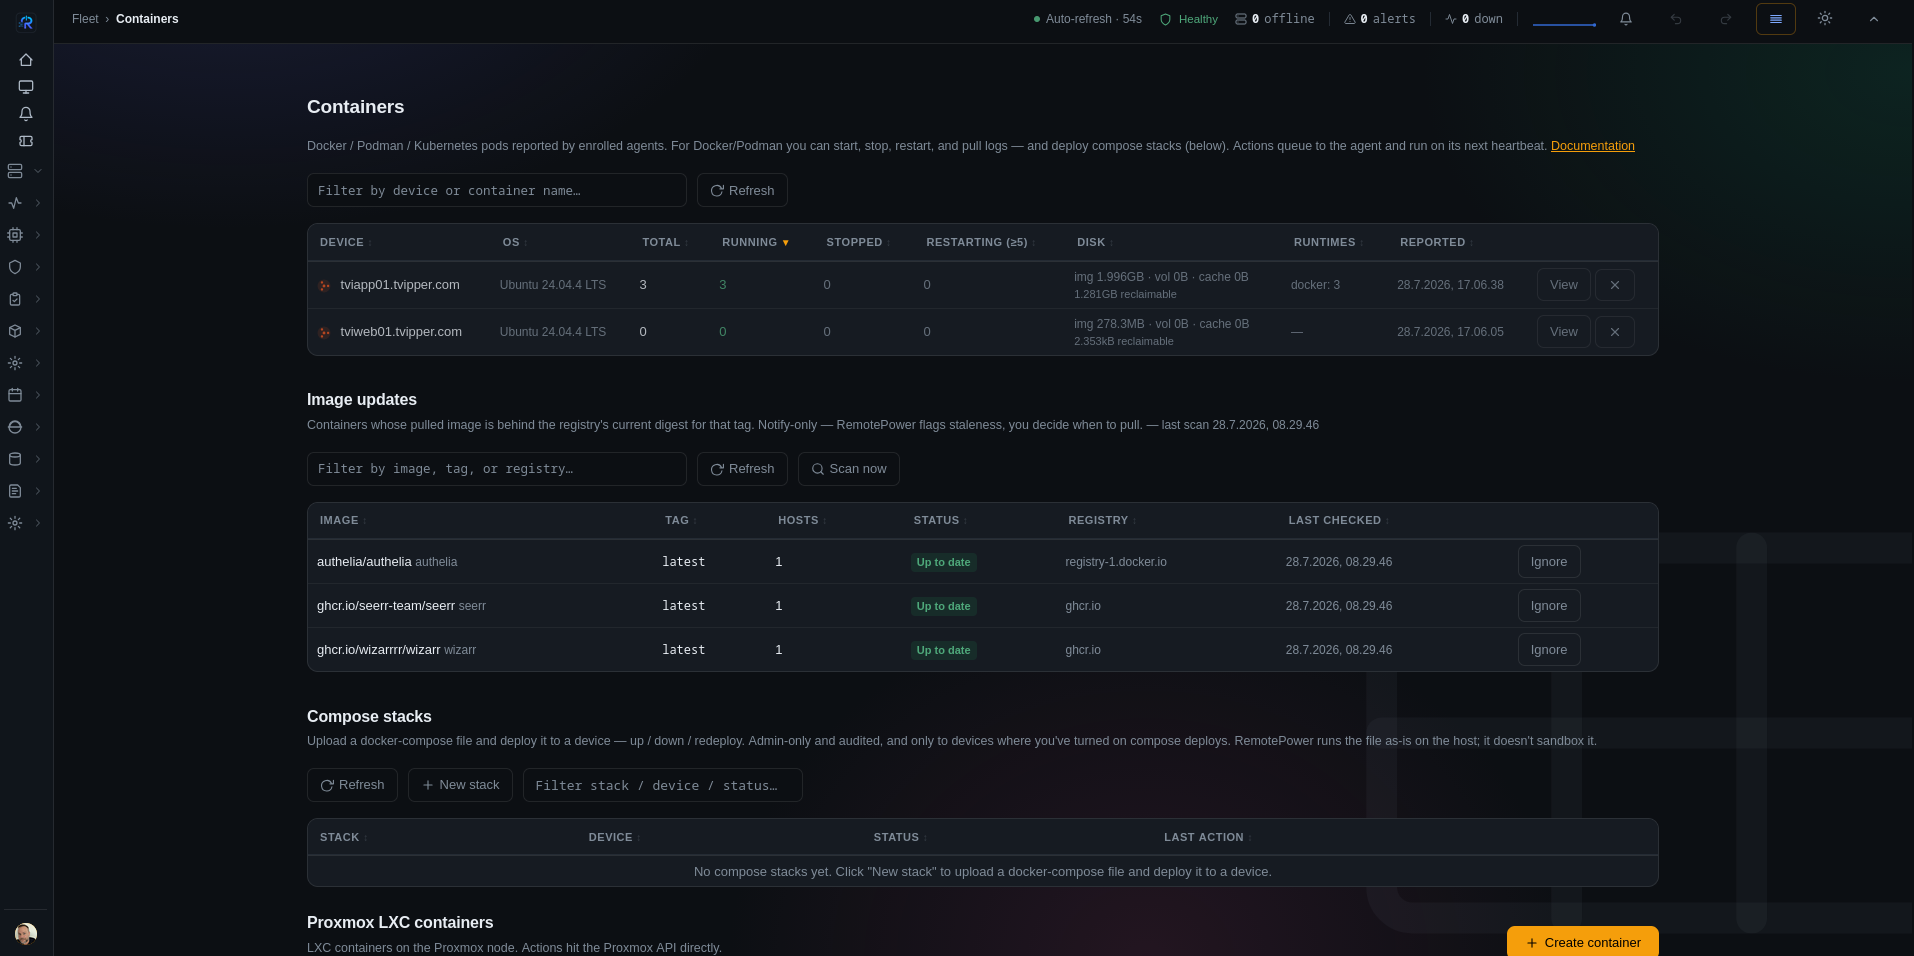
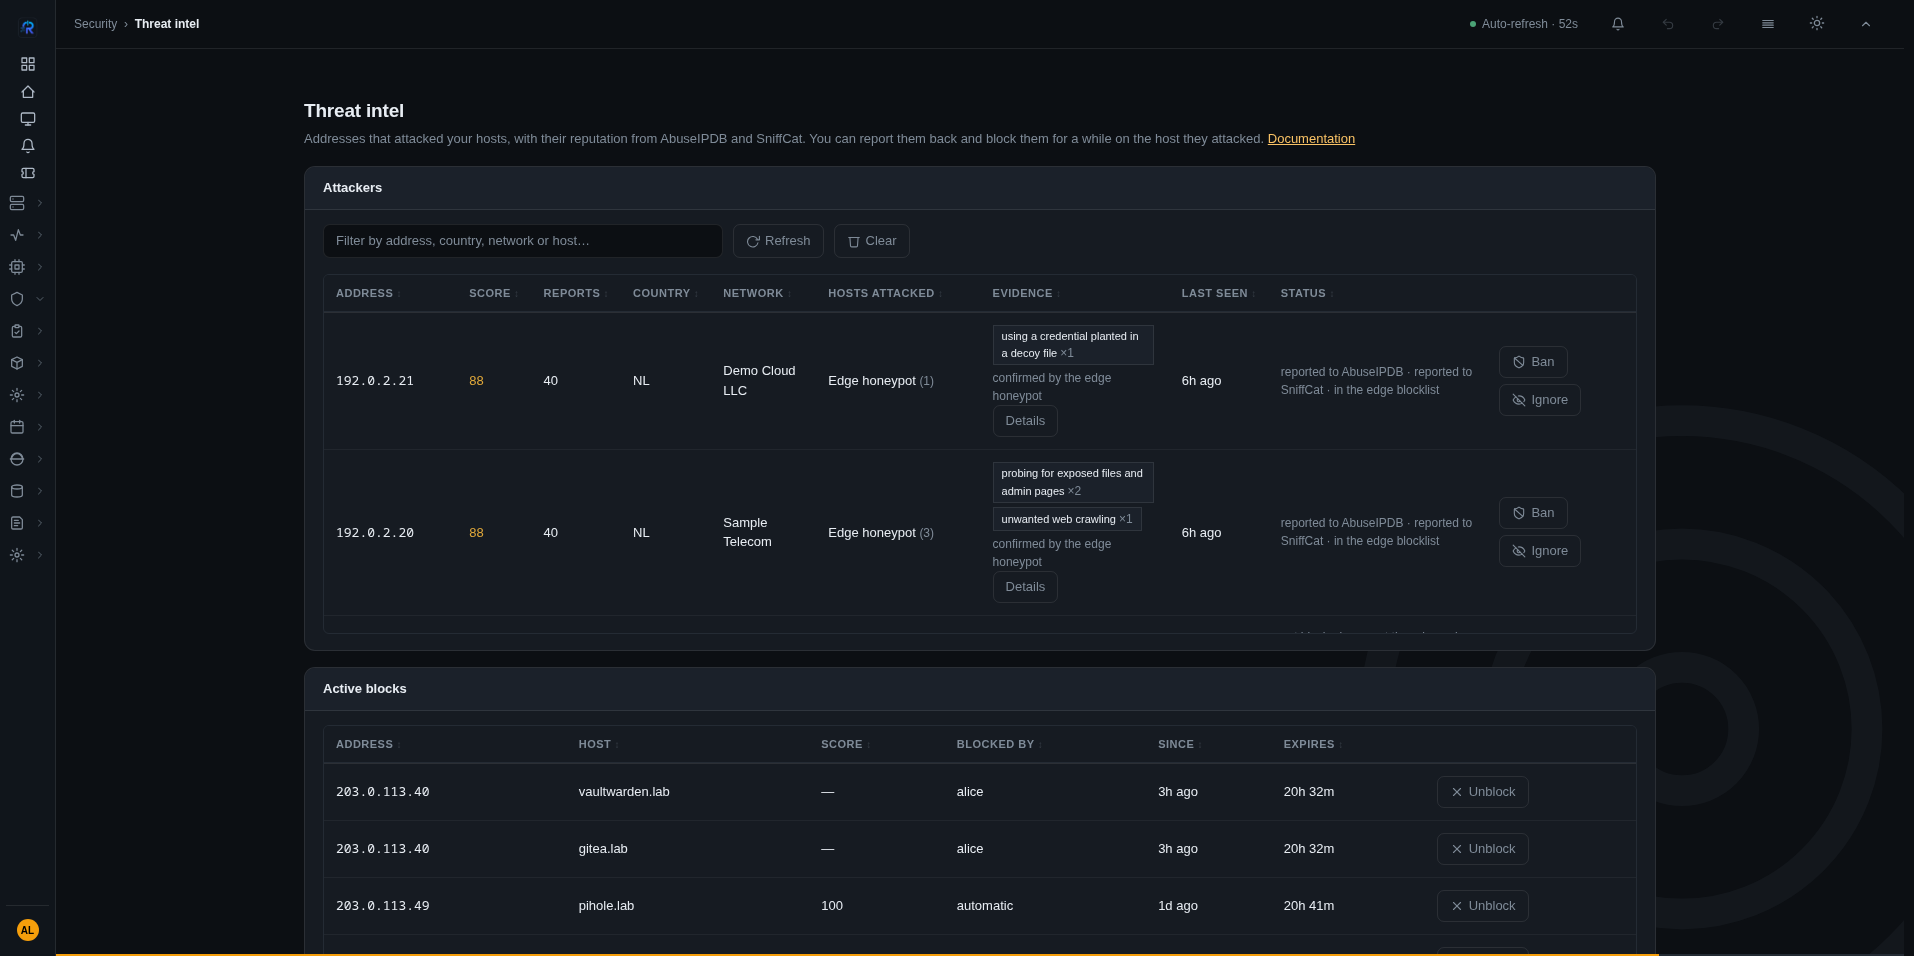
The edge, and the evidence. Threat intel used to learn about an attacker from your own hosts' logs. Cloudflare refuses requests before they reach a host, and a honeypot catches scanners no host log ever sees. Now RemotePower reads both and reports each address once, with the evidence behind it.
Read with a read-only token, on a Free plan too. Only a refusal that means an attack counts: challenges, country rules and IP access rules are set aside, and the page says how many and why. No path and no user agent is ever fetched.
An address the honeypot banned is reported at once. A credential the honeypot handed out being used, and a sign-in to a decoy service, are classes of their own.
Linux agents read nginx and Apache logs, ModSecurity, fail2ban, CrowdSec and the firewall's log, and send counts and fixed labels only. A report says what the address did, once per address however many hosts saw it.
One IP list built from your entries, what RemotePower found, and AbuseIPDB's and SniffCat's blacklists, so a rule of yours keeps blocking what they report. It writes the list and nothing else, and holds a sync that would empty or halve it.
Every attacker row has Ban and Unban. The edge half stops traffic that arrives through Cloudflare, the host half stops direct connections, and the dialog says which is which.
Lists of addresses and of kinds of attack that are never reported, and an Ignore button on each attacker. An ignored address is still recorded and blocked as before; only the public report is skipped. A Clear button forgets what was recorded and keeps blocks, bans and what the Cloudflare list uses.
A revoked token or a held list sync raises an alert and closes it when it recovers, instead of stopping the reporting in silence.
Twenty-three issues found and fixed before release, with a table of every tool that was run and what it said. It is the project's own review, and says so.
Relative times and the tips on the About page follow the interface language, and the tips now describe the pages that exist.
One script gets you nginx + a Python backend + an admin login. Add a host by running the agent installer and pasting a PIN. Stores everything in flat JSON by default — or grow into SQLite, then PostgreSQL with failover, read replicas and relay satellites when you reach thousands of hosts. No cloud account, your data stays yours.
RemotePower is self-hosted software you run yourself. The live demo is a read-only sandbox (log in with demo / demo).
 RemotePower